Security
Preventive.Security-first.Defense in depth.
Defense in depth that stops attacks early, specialized threat hunting across your environment, and resilience built in before you ever need it.


What you get
Monitored 24/7
24/7 detection and response.
Defense in depth
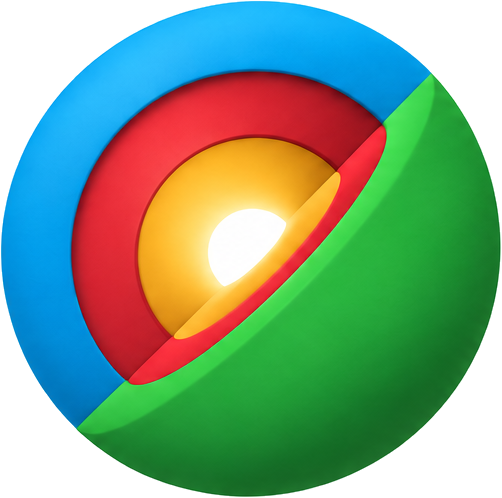
Four layers, each with its own job.
Threat hunting
Specialized threat hunting, when it's part of your plan.
Resilience built in
Immutable, ransomware-protected backups.
Leadership reporting
Reports your leadership can act on.


The work
Protect
We protect your people and email, devices and servers, identities and data. Security specialists monitor your environment 24/7, review the logs and act on what they find.
Threat hunting
Threat hunting is a specialized service. When it's part of your plan, our experts go looking for threats that never raised an alarm.
Resilience
Resilience is part of the design, with immutable, ransomware-protected backups, a continuity plan and clear roles agreed in advance. For organizations facing an active incident, our Cyber Security Incident Response team is ready to help.
Built around you
Our specialists help you find what your environment really needs, and we build coverage around what we agree on together, never a forced bundle.
Prevention stops the common attacks. Specialists hunt for the quiet ones. And resilience is built into every layer, so your business keeps moving.
Every layer has a job.
Network security
- Users and email
Stronger protection for Microsoft 365 email.
- Endpoints and servers
Endpoint protection, hardening, and finding and fixing weak spots.
- Identity and access
Protect passwords, admin rights and sign-ins, and harden Microsoft 365 against account takeover.
Data and resilience
Find your sensitive data and keep it from leaving, with immutable, ransomware-protected backups and a continuity plan.
- AI security: detection, response and governance for how your organization uses AI.
Threat hunting
Threat hunting is a specialized service. When it's part of your plan, our experts go looking for threats that never raised an alarm.


Services
Advanced Email Security
Stronger protection for Microsoft 365 and Google Workspace email.
Managed EDR
Protection for your covered desktops, laptops and servers, tuned with the vendor and monitored by our team.
24/7 Detection and Response
Monitoring, detection and response across devices, email, identities and network, scoped to your agreement.
Identity & Access Security
Protect passwords, admin rights and sign-ins, and harden Microsoft 365 against account takeover.
Every plan is built with you and can extend across every layer in the rings above, including backup and recovery with immutable, ransomware-protected backups. Ask us about the full picture in your consultation.
See what your leadership will see.
Executive security reporting in plain language: what we watched, what we found and what we fixed, built for executives and boards. The scorecard below is a sample made for a fictional company.


How it works
Assess
We talk through your environment, the tools you already own and your priorities, then give you a ranked list of the weak spots to fix first.
Design and deploy
Together we agree on what's monitored, whether specialized threat hunting belongs in your plan, and the response authority in your agreement. Then we install and tune our security tools on your covered devices.
Operate and report
We monitor 24/7, coordinate fixes with your team and send reports your leadership can act on.
What changes for you
- Fewer easy ways in, because weaknesses are found and fixed on a steady cycle.
- Specialists watching 24/7, connecting alerts from devices, email, identities and the network into one picture.
- A written agreement on who acts, when, and how far.
- Resilience planned in from day one, not added after.
FAQs
We already have antivirus. Isn't that enough?
Antivirus is one layer. Many attacks start with an email or a stolen login, so we connect protection across devices, email, identities and the network, and our specialists review what it shows.
What hours do you monitor?
Our specialists monitor around the clock and respond within the authority and hours set in your agreement. What we're authorized to do when we find something, from alerting you to containing a threat, is written into your agreement and confirmed before you sign.
Can you work with our existing security provider?
Yes. We can work co-managed, including taking escalations from your current managed detection provider and acting on them within the authority set in your agreement.
Do you handle compliance?
We don't certify compliance for you. Our services put in the controls and reporting that support your compliance work, and your team stays the owner.
Is backup included?
Backup is an optional service, not part of every plan by default. If we agree on it together during your assessment, it runs as Backup & Disaster Recovery within our security services, with resilience built in through immutable, ransomware-protected backups. Managed IT then checks that your server backups complete and fixes any that fail.
See where your defenses stand.
Find out where your layers are strong and where they're thin, and what our specialists would do first.