Under cyber attack? Tap to call incident response.

Under cyber attack right now? Call our incident response team at +1 877-509-2673.

Get incident help

Advisory · Virtual CISO

Security leadership without waiting on a full-time hire.

A senior security leader for your organization (often called a virtual CISO) who sets priorities, frames risk decisions and reports to your leadership. No other InnerCore services required.

See sample reporting

Layered security roadmap panel: a shield linked to a board of five lanes for where you stand, priorities and a roadmap, risk decisions, leadership reporting and regular review.

The work

Security leadership without a full-time hire. Your advisor sets the security agenda with you, frames the risk decisions leadership has to make, and reports progress in plain language.

Advisory doesn't require any other InnerCore service. Your advisor helps you pin down what you really need, and we build the engagement around it.

When organizations bring in security leadership

  • The board or investors ask "are we secure?" and no one can answer clearly.

  • A large customer, partner or insurer wants to see a security program.

  • Security work is happening, but nobody owns the priorities.

  • You've had a scare and want a plan, not just fixes.

  • You need leadership now and aren't ready for a full-time hire.

What your advisor does

  • Where you stand

    We review where your security is today and how it's reported to leadership.

  • Priorities and a roadmap

    We agree priorities and a security roadmap with your leadership.

  • Risk decisions, framed

    The decisions leadership has to make, set out in plain terms with the trade-offs.

  • Reporting leadership can follow

    Executive security reporting on progress and risk, written for executives and boards.

  • Regular review

    We meet regularly to review risk and progress and adjust the roadmap.

Leadership and operations, connected

A security program needs direction and delivery. Your advisor sets the direction: the priorities, the roadmap and the reporting. The work itself is carried out by your own team, your existing providers or InnerCore's security services, whichever your organization has in place. Progress comes back to your advisor, so leadership sees one honest picture of where security stands.

How it works

  1. Assess: We review where your security stands today and how it's reported.

  2. Prioritize: We agree on priorities and a security roadmap with your leadership.

  3. Review: We meet regularly to review risk and progress.

See what your board will see.

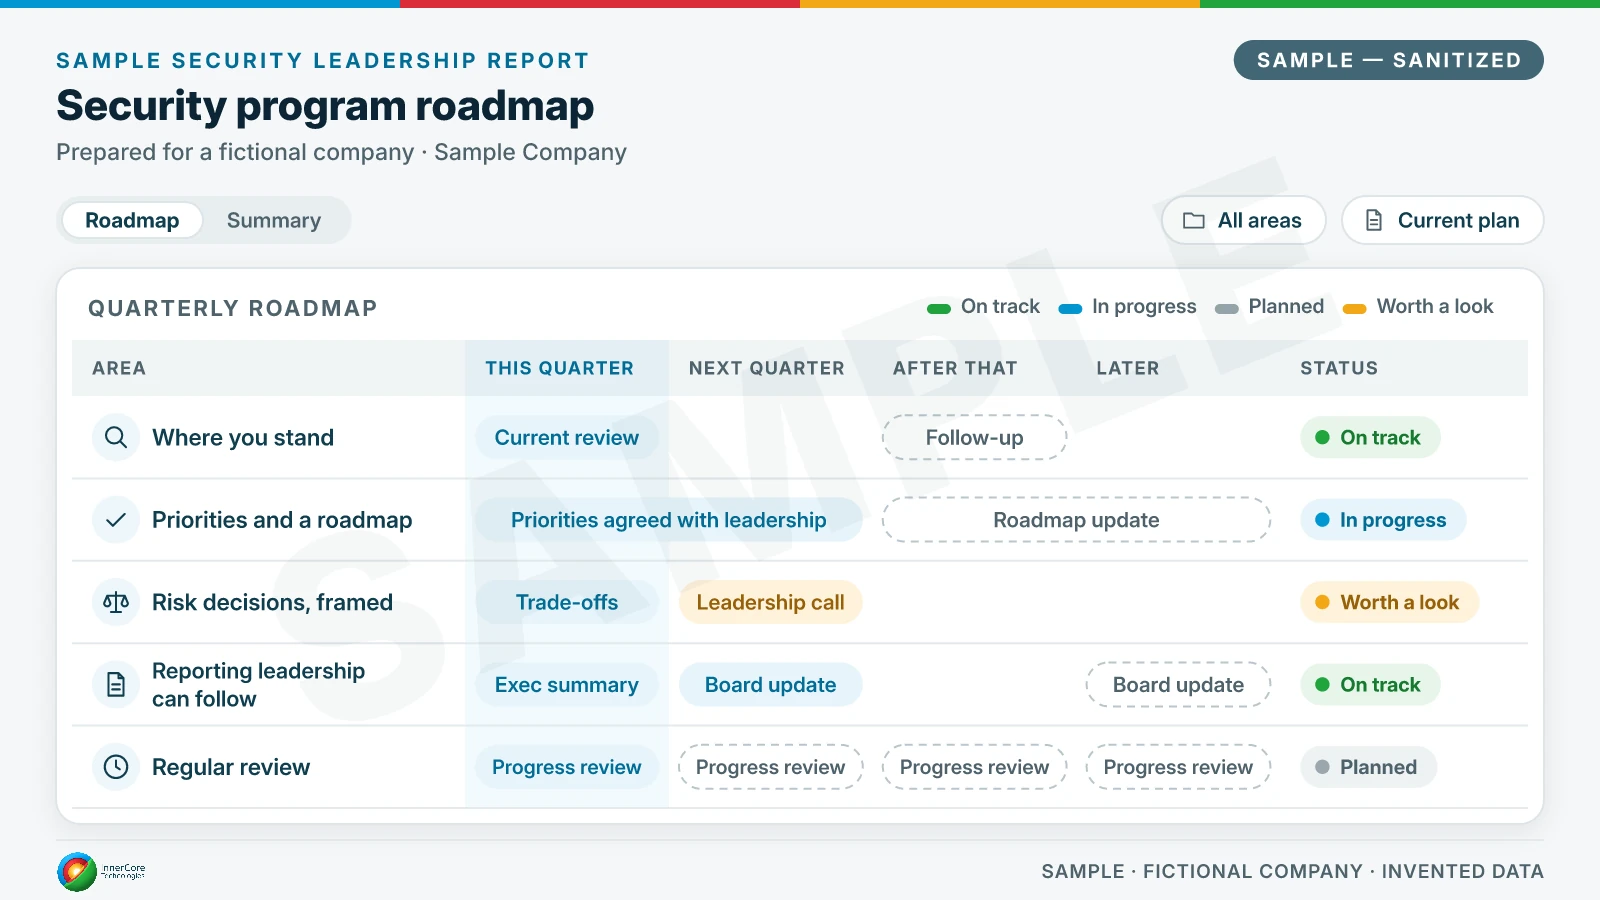
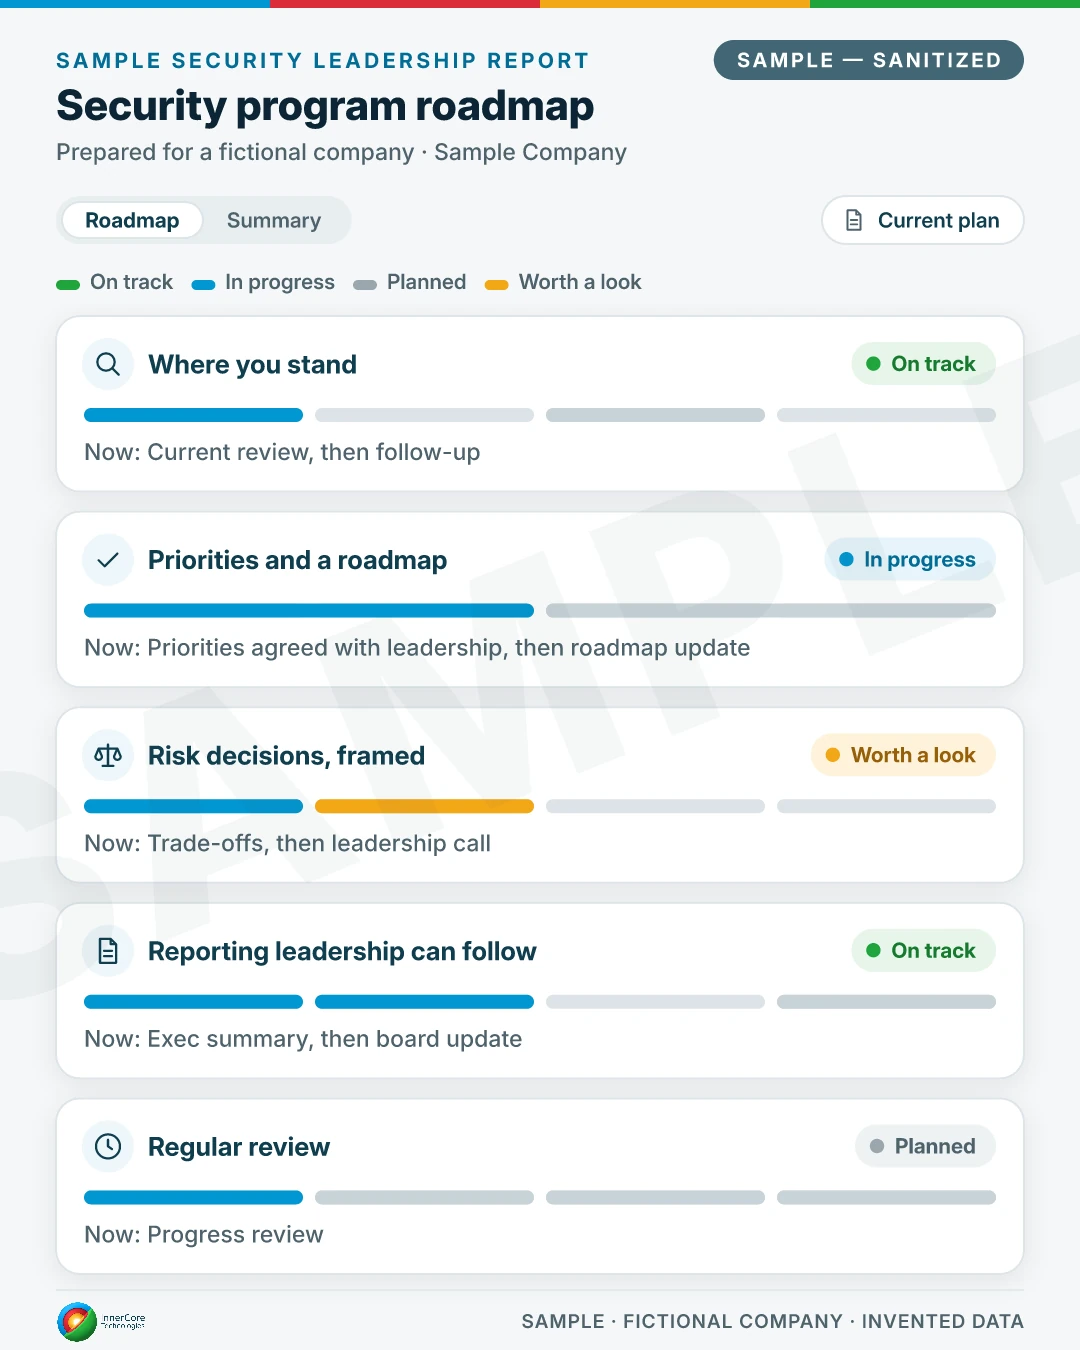
Executive security reporting in plain language: where security stands, what's moved since last time and which decisions need leadership. The roadmap below is a sample made for a fictional company.

Sample security program roadmap for a fictional company: five areas (where you stand, priorities and a roadmap, risk decisions, leadership reporting and regular review) laid out across this quarter, next quarter, the following quarter and later, each marked on track, in progress, planned or worth a look.

vCISO or full-time CISO?

  • Commitment

    vCISO
    Senior leadership without a full-time hire
    Full-time CISO
    A permanent executive role
  • Getting started

    vCISO
    No executive search
    Full-time CISO
    A search, then onboarding
  • Perspective

    vCISO
    Brings an outside view to your priorities
    Full-time CISO
    Deep inside knowledge over time
  • Best for

    vCISO
    Organizations building or resetting a security program
    Full-time CISO
    Organizations whose size and risk need a dedicated executive

Many organizations bring in a vCISO first and decide later whether a full-time role makes sense.

Is it a fit?

Where security leadership fits best

  • Leadership wants a clear security agenda and someone to own it.
  • You have security tools or a provider, but no one setting direction.

When our specialists will point you to another service

  • You need experts watching your environment day and night → 24/7 Detection and Response
  • You need technology plans and budgets beyond security → IT Strategy & Budgeting

EXAMPLE scenario

EXAMPLE: illustrative only, not a real customer.

Problem

A manufacturer's leadership kept asking whether the company was secure, and the answers were a list of tools.

What we did

Our security advisor reviewed where security stood, agreed priorities and a roadmap with leadership, and reported progress in plain language.

Outcome

Leadership has a ranked plan, knows which risks it has accepted, and can answer the board's question with confidence.

What changes for you

  • A senior security voice at the leadership table.
  • A ranked roadmap in place of a list of tools.
  • Risk decisions made knowingly, with the trade-offs written down.
  • Clear answers when the board asks "are we secure?"

FAQs

How is a vCISO different from a full-time CISO?

A vCISO gives you senior security leadership without a permanent executive hire. A full-time CISO is a dedicated role inside your company. Which fits depends on your size, your risk and how much leadership time security needs.

Do we need a vCISO if we already have a security provider?

They do different jobs. A provider runs security operations. A vCISO sets the direction, priorities and reporting that those operations should follow.

Is a fractional CISO the same thing?

Yes. Fractional CISO, virtual CISO and CISO as a service all describe senior security leadership without a full-time hire.

Do we have to use other InnerCore services?

No. Security leadership stands on its own. Your advisor works with the team and providers you already have.

Does your security advisor hold an officer position?

No. Our advisors don't hold a director or officer position in your company and take on no fiduciary role.

Does security leadership make us compliant?

No. We don't certify compliance. Security leadership supports your compliance work, and your team stays the owner.

Put security on the leadership agenda.

Talk with us about security leadership: where your program stands, what leadership needs to decide and how progress gets reported.

This site uses analytics cookies only if you accept. Privacy policy