Under cyber attack? Tap to call incident response.

Under cyber attack right now? Call our incident response team at +1 877-509-2673.

Get incident help

Security · Detect and respond

24/7 Monitoring, Detection and Response

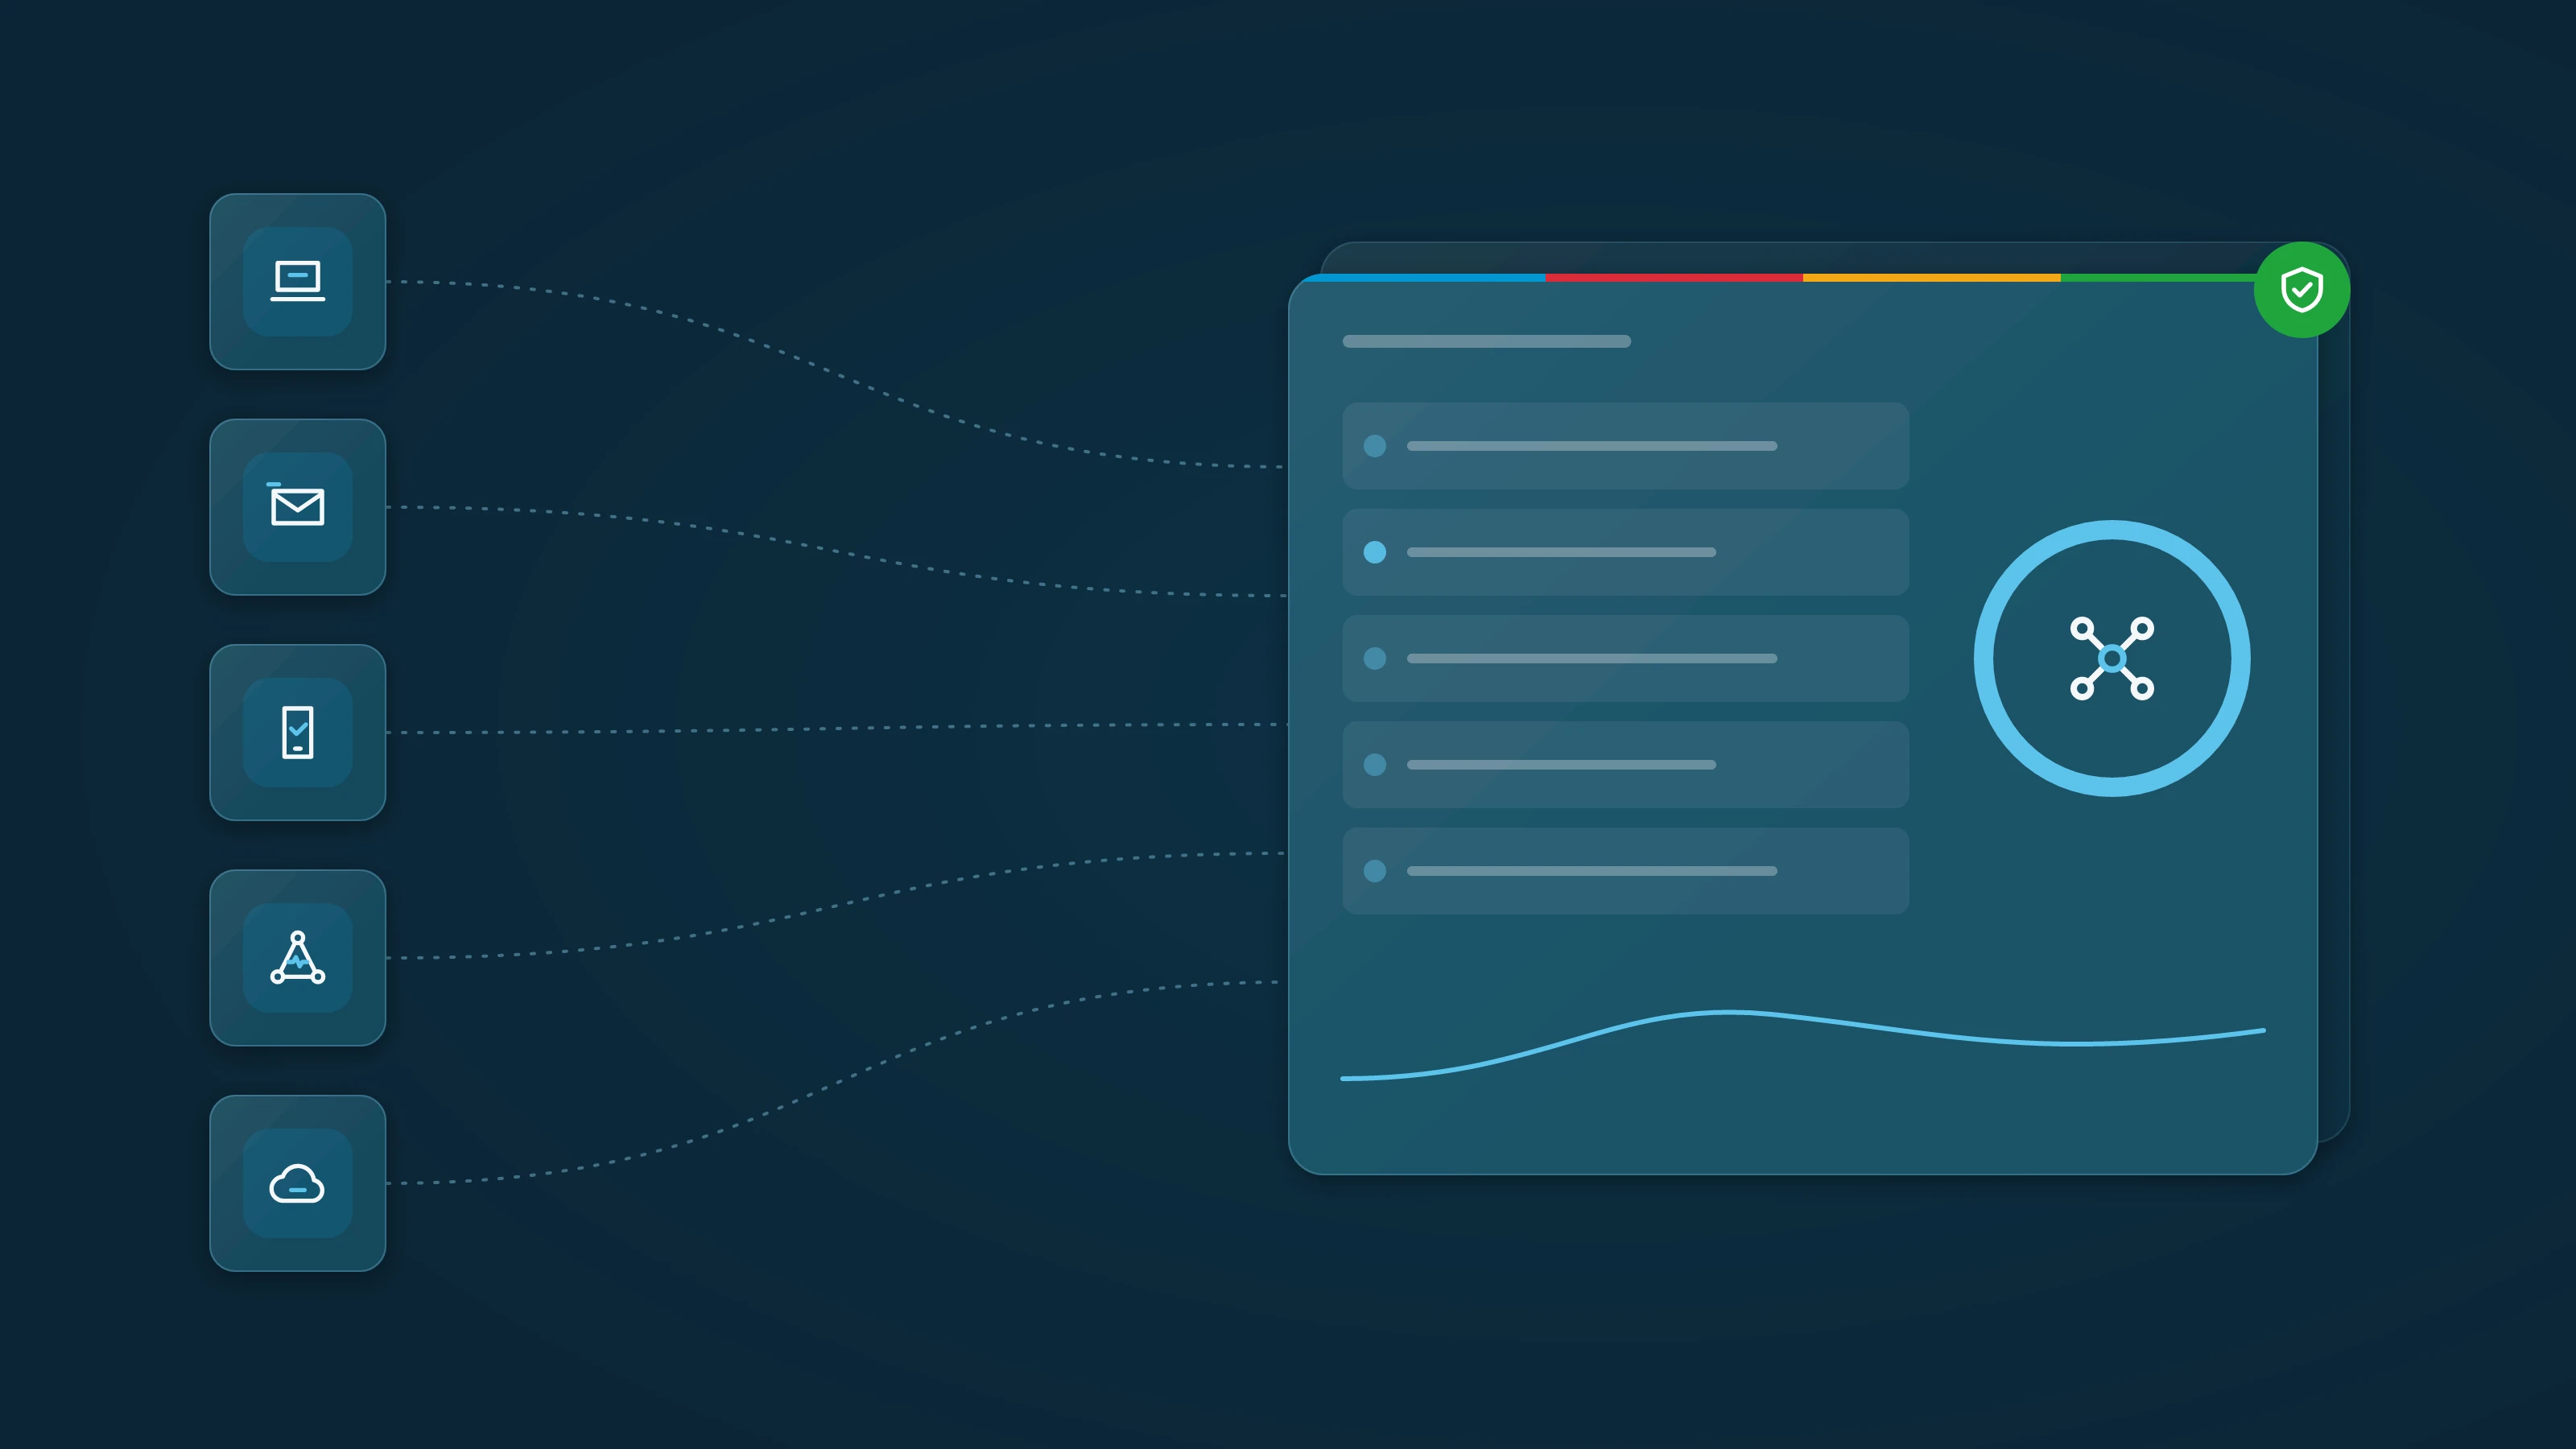
Security tools produce alerts. Managed detection and response (MDR) puts specialists behind them, connecting signals from your devices, email, identities and network into one picture, plus Microsoft 365 and cloud environments where your plan includes it, investigating what matters and acting within the authority in your agreement.

See how it works

What's at stake without it.

Attackers move between devices, accounts and cloud apps. If no one connects those signals, the business pays for the delay.

  • Weaknesses used against you.

    Unpatched systems, exposed edge devices and VPNs give attackers a way in that looks like normal traffic until someone connects the dots.

    Exploitation of vulnerabilities was the way in for 20% of breaches in Verizon's 2025 report, up 34% on the year before.

    Verizon 2025 Data Breach Investigations Report

  • Risk that arrives through partners.

    Suppliers, software providers and service partners connect to your systems. A problem in their environment can become activity in yours.

    A third party was involved in 30% of breaches, double the year before.

    Verizon 2025 Data Breach Investigations Report

  • Alerts no one connects, and questions from the board.

    A strange sign-in in one console and an odd process in another look minor on their own. Leadership, insurers and auditors want to know who is watching and what happens when something is found.

Larger organizations aren't exempt. Ransomware was part of 39% of breaches at larger organizations. Verizon 2025 Data Breach Investigations Report

Are security tools on their own enough?

EDR, a SIEM and Microsoft 365's built-in alerts are essential, and we build around the ones you already own where they fit. But tools on their own produce alerts. They don't decide which ones matter, connect them across layers or take action. MDR is the service that does: specialists who watch what the tools show, investigate and respond within the authority written into your agreement.

  • Alerts

    Security tools only
    Each tool raises its own alerts in its own console
    Tools plus MDR from InnerCore
    Signals from your devices, email, identities and network — plus Microsoft 365, and cloud environments and third-party logs where your plan includes them — collected in one place
  • Context

    Security tools only
    A sign-in and a device process are seen separately, if at all
    Tools plus MDR from InnerCore
    Related signals are correlated, so a strange sign-in and an odd device process are seen together
  • Who reviews

    Security tools only
    Whoever on your team has time, between other priorities
    Tools plus MDR from InnerCore
    Security specialists triage and investigate every escalated alert
  • Acting on a threat

    Security tools only
    Depends on someone noticing and knowing what to do
    Tools plus MDR from InnerCore
    Response within the authority and hours set in your agreement, for example isolating a device or securing an account
  • Investigation

    Security tools only
    An alert shows what happened on one system
    Tools plus MDR from InnerCore
    Specialists trace related activity across devices, accounts and logs to find where it started
  • Reporting

    Security tools only
    Raw logs and dashboards
    Tools plus MDR from InnerCore
    Reports leadership can read: what was investigated, what was found and what changed

Monitored around the clock, with response within the authority and hours set in your agreement.

Your environment is monitored around the clock, with response within the authority and hours set in your agreement. Our specialists investigate anything suspicious and act within that authority — for example isolating a device or securing an account. Before you go live, we agree what's monitored, who on your side we contact and what we're allowed to do first. When we act, we tell you what we found and what we did.

Response hours and the exact actions in your authority level are written into your agreement and confirmed before you sign.

What you get

One managed service that turns signals into decisions.

  • Signal collection.

    We connect signals from your devices, email, identities and network, plus Microsoft 365, and cloud environments and third-party logs, including firewall logs, where your plan includes them.

  • Correlation.

    A security information and event management (SIEM) platform connects related events across layers into one picture, so patterns stand out.

  • Analyst triage.

    Security specialists review escalated alerts, investigate what they mean and separate real threats from noise.

  • Response actions.

    We act within the response authority in your agreement, for example isolating a suspicious device or securing an account showing suspicious sign-in activity.

  • Reporting.

    Reports on what was investigated, what was found and what changed, with an executive summary for leadership.

  • Threat hunting.

    A specialized service. When it's in your plan, our experts search your environment for attacker activity that never raised an alert.

Signals in, decisions out.

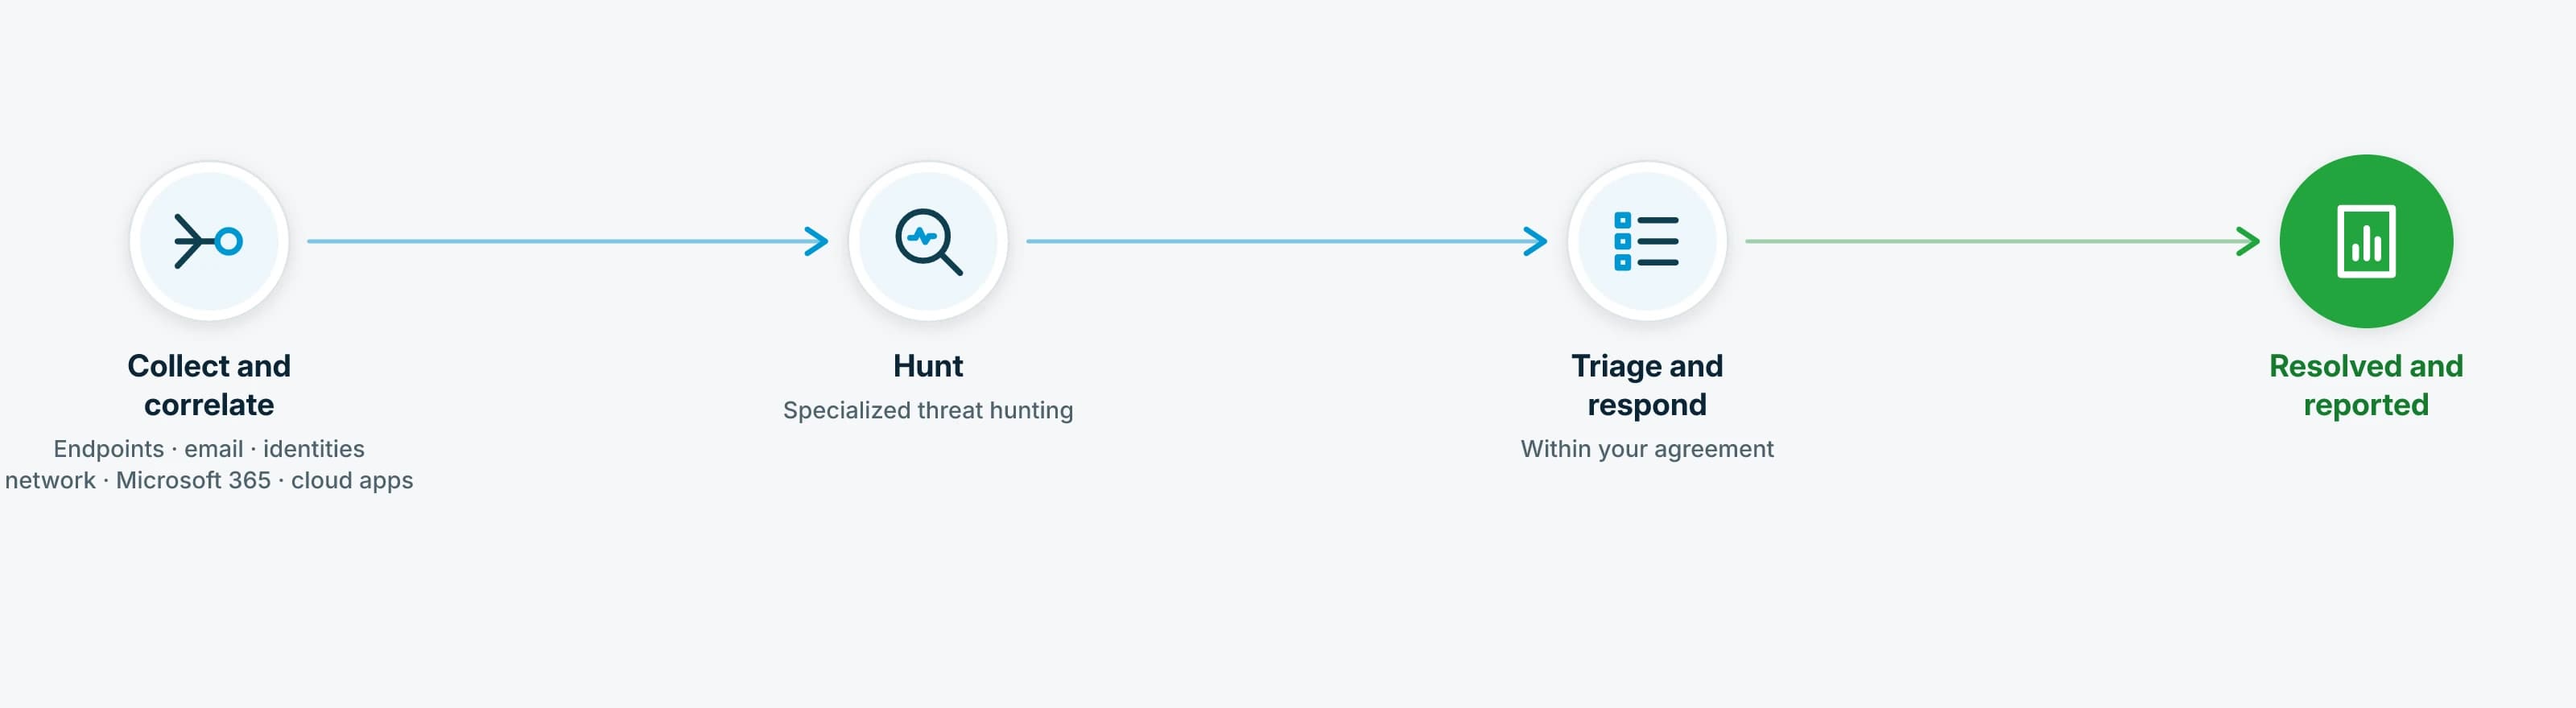
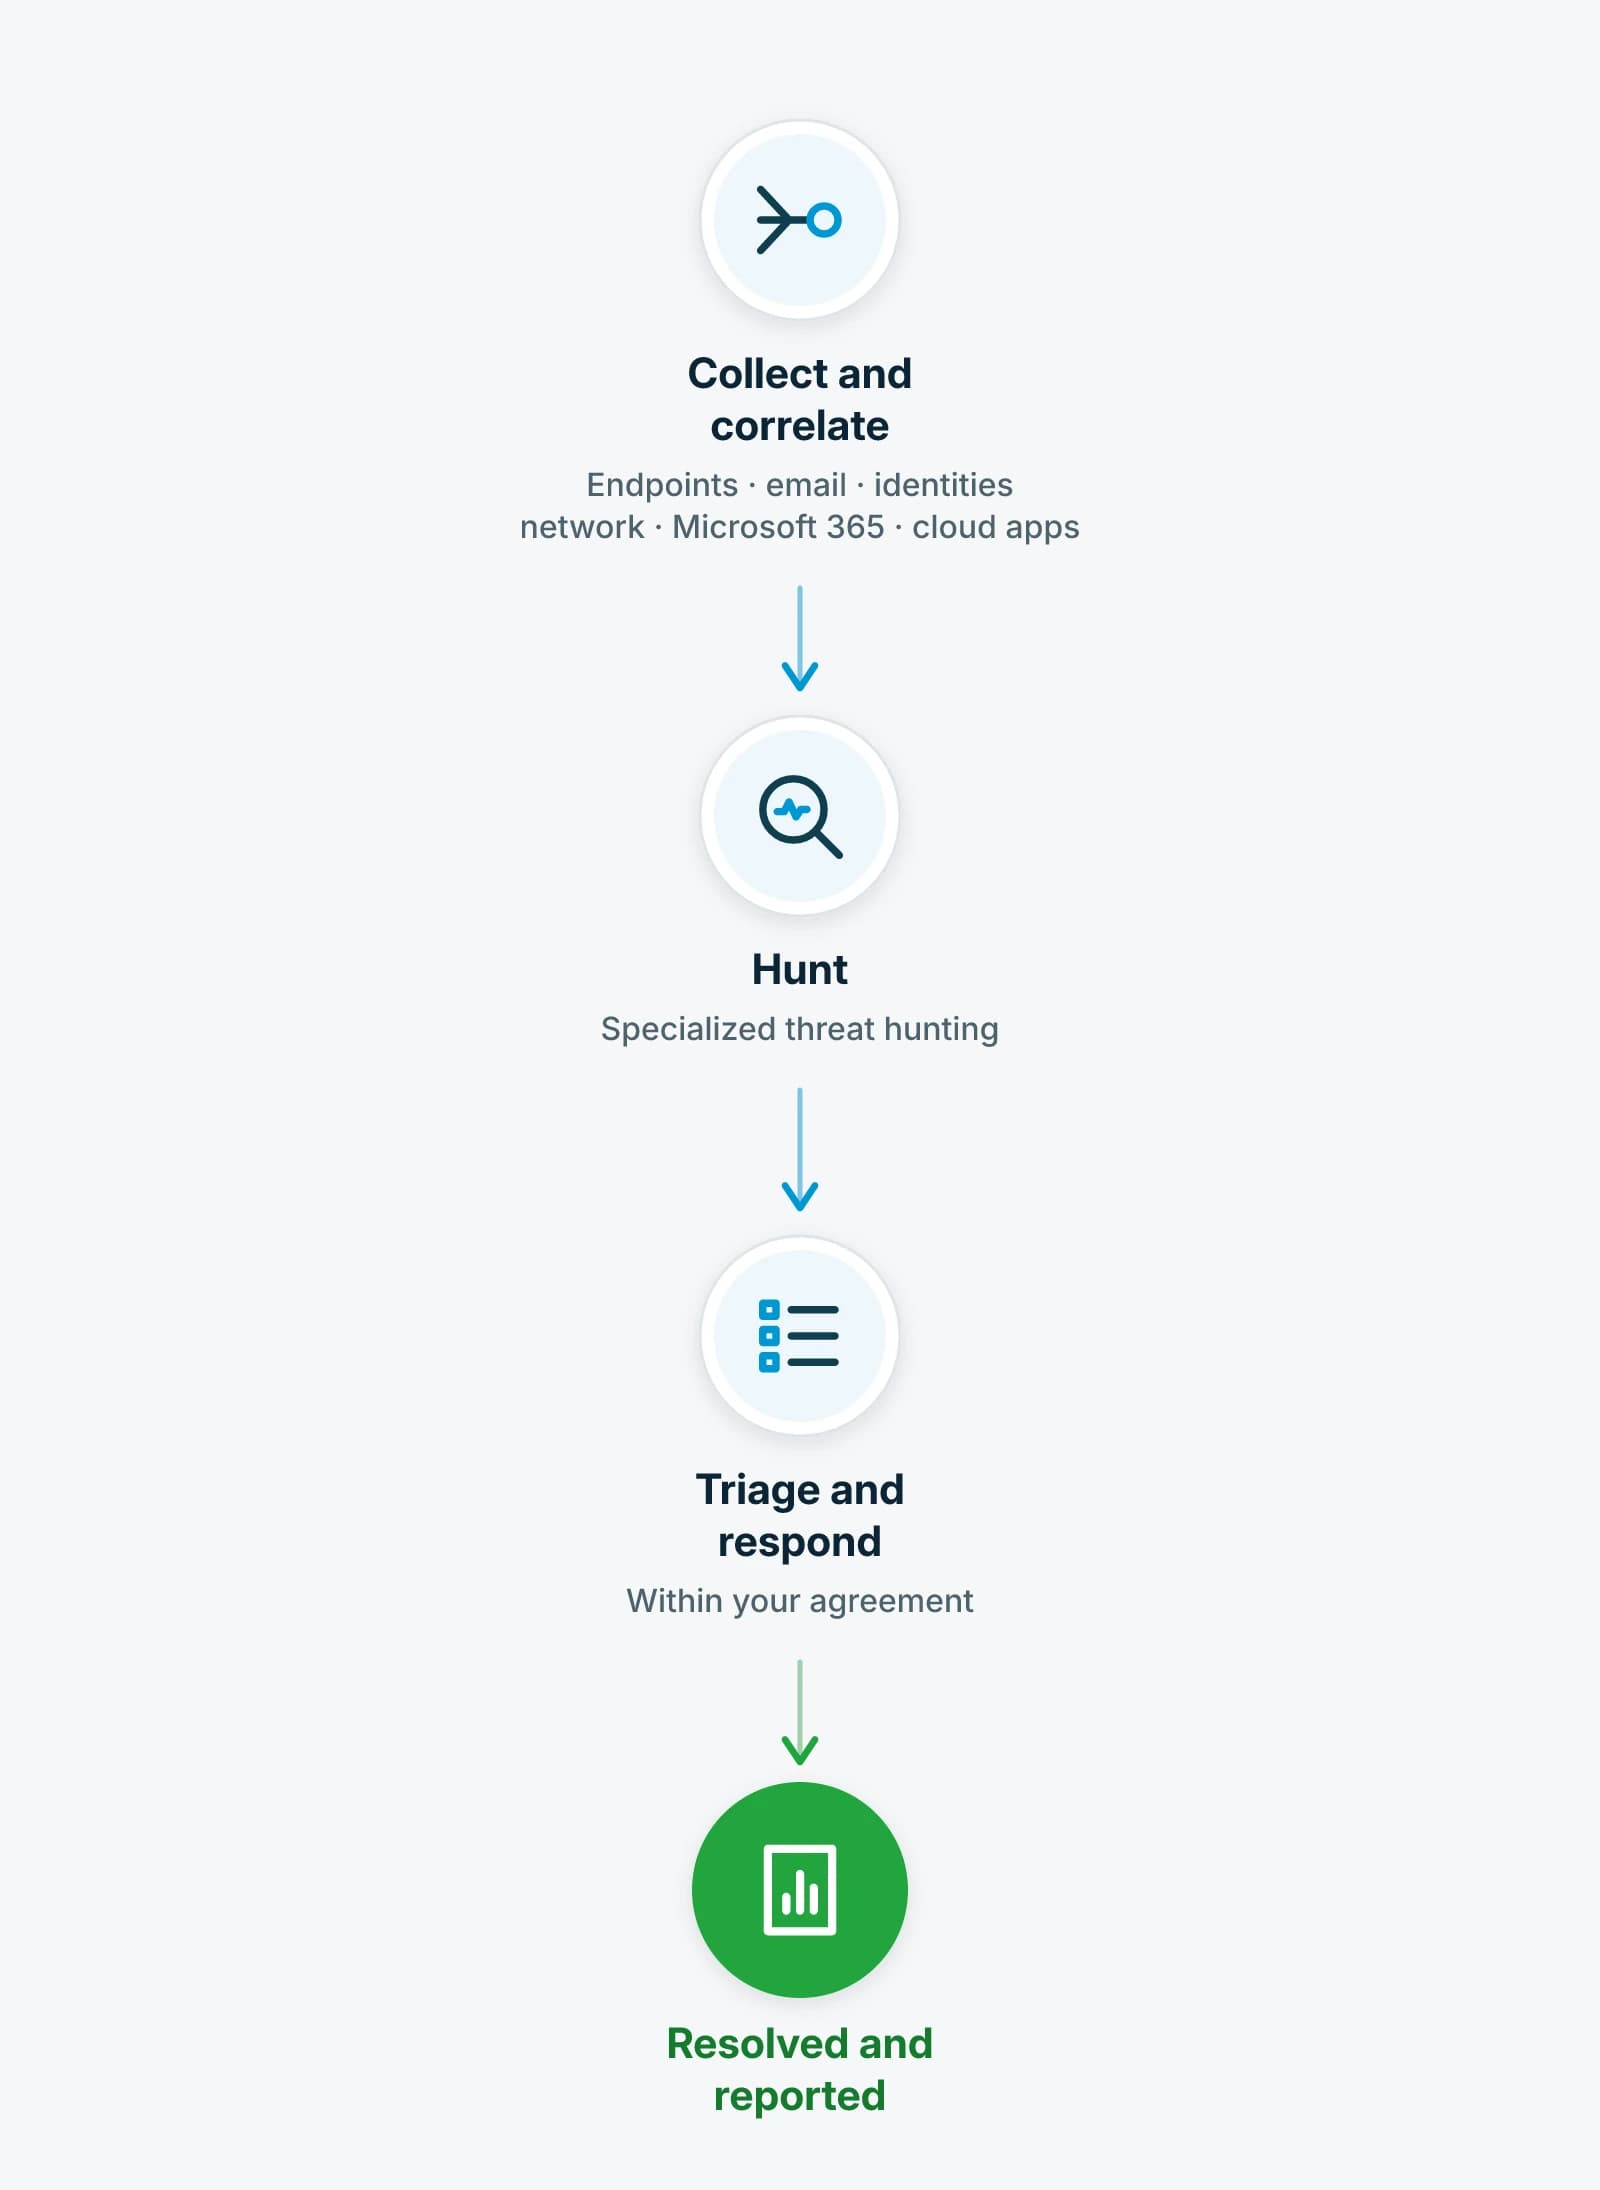
Signals from your devices, email, identities and network — plus Microsoft 365 and cloud environments where your plan includes it — are collected and correlated. Specialized threat hunting, when it's in your plan, looks for activity that never raised an alert. Specialists triage, investigate and respond within the agreed authority. Each case ends resolved and reported.

Looking for what never raised an alarm.

Some attacker activity is built to look normal and never trips a rule. Threat hunting is a specialized service: when it's part of your plan, our experts search your environment across every layer for signs of that activity, and what they find feeds straight into response and vulnerability management. It can be included in a managed security agreement or added as a retainer.

We build on industry-leading, best-of-breed security platforms, and when one isn't the right fit for your environment, our specialists vet and deploy one that is.

You don't have to start over. Our specialists build around the security tools you already own where they fit, and recommend what your environment needs as part of a plan we agree on together. Never a forced bundle.

What we can do on your behalf

  • Notify and advise

    What it means
    We tell you what we found and what to do.
    Example actions
    Written findings with clear next steps
  • Guided response

    What it means
    We work through the response with your team.
    Example actions
    Walking your team through isolating a device or securing an account
  • Authorized containment

    What it means
    We act on agreed assets and events without waiting.
    Example actions
    Isolating a suspicious device from the network; securing an account showing suspicious sign-in activity
  • Incident response

    What it means
    A separate engagement for a major incident.
    Example actions
    Cyber Security Incident Response

The level, and the exact actions in it, are written into your agreement and confirmed before you sign.

How you'll hear from us

Before you go live, we agree who on your side we contact, for what kinds of events, and what we're allowed to do first. When we act, we tell you what we found and what we did. Reporting covers what was investigated, what was found, which privileged accounts were watched, and an executive summary your leadership can read.

Works with what you have

You don't have to start over. We build around the security tools you already own where they fit. If you already have a managed detection provider you trust, keep them: we can take the escalations they raise and act on them within the authority set in your agreement.

Example

EXAMPLE: illustrative only, not a real customer.

Problem

A covered laptop at a distribution company began running a process that tried to reach other machines on the network.

What we did

Under the authorized-containment level in the agreement, our specialists isolated the device from the network, investigated, cleaned it up and returned it to service.

Outcome

The company's IT lead had a written summary of what happened, what we did and the one setting to change so it doesn't recur.

FAQs

How is MDR different from EDR or a SIEM?

Endpoint detection and response (EDR) is a tool on your devices. A security information and event management system (SIEM) collects and connects logs. Managed detection and response (MDR) is the service: people who watch what those tools show, investigate and act.

What hours do you monitor and respond?

Your environment is monitored around the clock, with response within the authority and hours set in your agreement. We confirm exactly what applies to you before you sign.

What can you do without asking us first?

That's set by the response authority level we agree: notify and advise, guided response, authorized containment for defined assets and events, or a separate incident response engagement.

Is threat hunting a separate service?

Threat hunting is a specialized service. It can be included in a managed security agreement or added as a retainer, and our specialists will tell you whether it belongs in your plan.

We already have an MDR provider. Do we need this?

Keep them if they work for you. We can take the escalations they raise and act on them within the authority set in your agreement.

Should we build our own in-house security monitoring team instead?

Some large organizations build a security operations center (SOC) of their own. It means hiring and keeping analysts around the clock, plus the tools and processes behind them. A managed service gives you expert coverage without carrying all of that yourself.

Find out who is watching your environment.

Let's look at your detection and response together: which signals you collect today, who reviews them, and what our specialists would connect first.

This site uses analytics cookies only if you accept. Privacy policy