How We Work
How we work: clear scope, clear roles, clear reporting.
How we onboard, who does what, how often we review, and what you receive.
What changes for you
- You know what is covered, and up to what quantities.
- Shared responsibilities written down activity by activity (Lead / Support / Informed).
- Regular reviews: operational, security and risk, resilience, and executive.
- Reports that turn technical findings into decisions.
The work
Every engagement starts with written scope and a structured onboarding. From there we work to an agreed rhythm of reviews and reporting, so priorities, risks and the roadmap stay in front of you.
Offerings
What onboarding delivers
Kickoff meeting and onboarding plan with named contacts and a communication cadence
Deployment of InnerCore monitoring, management and security agents, with a coverage report
Documentation of your current environment
Network, servers, Active Directory, Microsoft 365 and DNS
An initial security baseline and vulnerability findings summary with prioritized recommendations
Configuration of email security and password management platforms, as proposed
A transition record from your current provider
Tools removed, credentials and access handed off
An onboarding completion summary and a service desk go-live notice to your users
We help you work out the coverage you really need and build services around it.
How it works
Kickoff and discovery: We confirm contacts and access, gather your documentation and record where your security stands today.
Deployment: We install our monitoring, management and security tools and set up your policies.
Transition: We work with your current provider, remove old tools and confirm everything is covered.
Go-live and review: We open the service desk to your people, send your onboarding summary and hold your first account review.
Ongoing: We assign a dedicated senior account manager and hold regular account reviews.
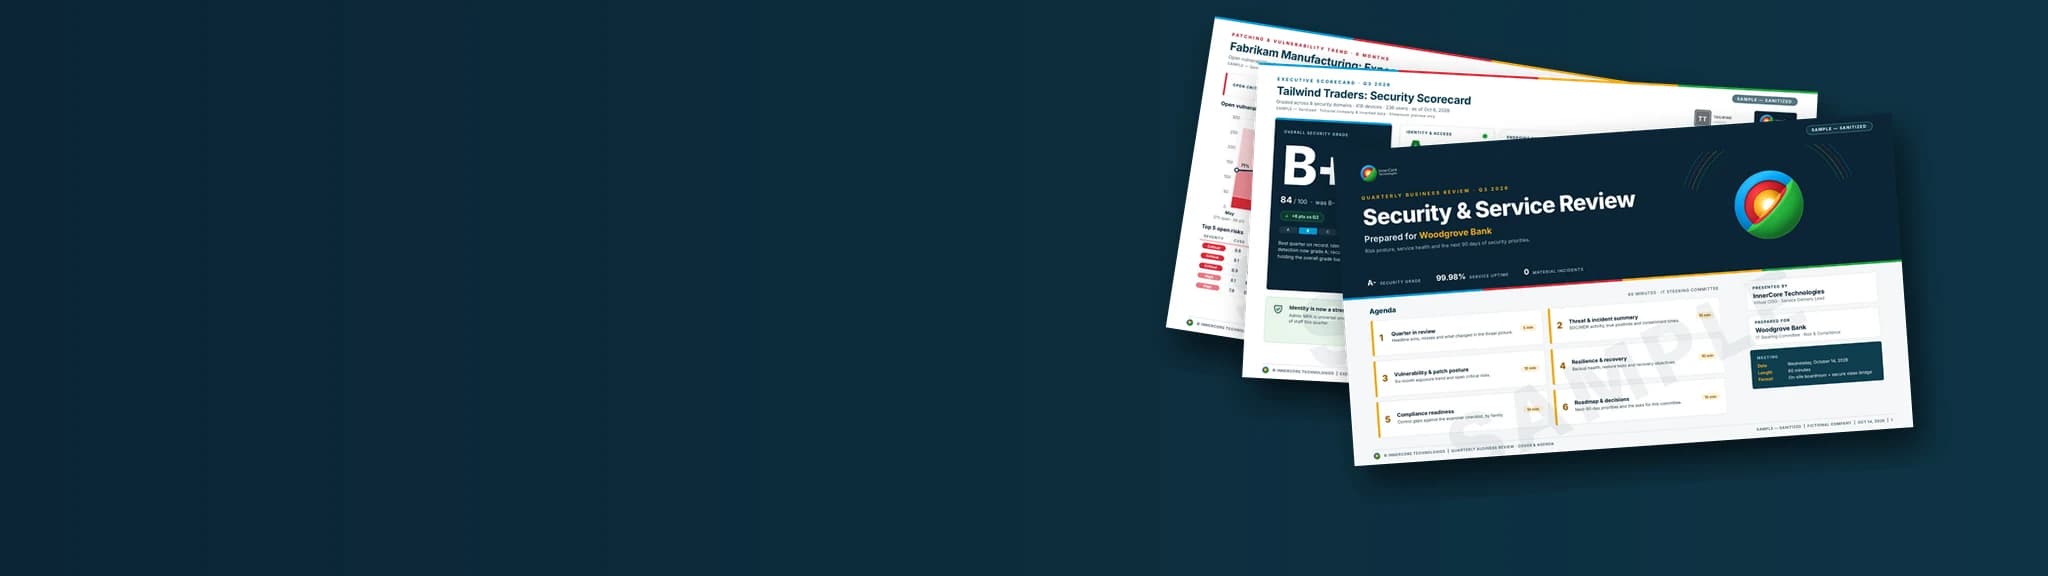
Sample reporting
Governance cadence
Operational review
Tickets, incidents, availability, changes, capacity
Security & risk review
Cases, vulnerabilities, response, risks, exceptions
Resilience review
Backup health, recovery readiness, tests
Executive advisory
Priorities, roadmap, investment, lifecycle, cyber risk. Cadence per agreement
FAQs
What do you need from us?
A primary contact who can approve changes, administrative access, existing documentation and vendor contacts, and a letter of authorization where vendors need one.
How do we accept onboarding?
Onboarding is complete when agents and platforms report on covered devices (or exceptions are documented), monitoring and service desk intake are live, legacy tools are removed and you receive the completion summary.
What do your reports look like?
One-page executive snapshots with key measures, a single visual and three takeaways. The sample shown is for a fictional company, with made-up data.
What happens with work outside our agreement?
We quote it, you approve it first, and we run it as a separate project.
See how we'd work with you.
Book a consultation and we'll walk you through onboarding.