AI Security & Governance · Guardrails
AI Usage Control: Guardrails for AI Use
Rules on paper don't change behavior on their own. AI Usage Control puts guardrails around how your people use AI tools, through a platform InnerCore implements and manages for you, the same platform that supports AI Detection & Response.
From policy to practice, managed for you.
In businesses without controls, AI rules exist only as a document people may or may not read. AI Usage Control closes the gap between what leadership decided and what happens day to day. We implement the platform in your environment, configure it to reflect the rules your leadership sets and manage it from then on. It shows which AI tools are in use and, where your plan includes it, holds back the ones you haven't approved and masks or stops sensitive information before it's shared. Because it also supports AI Detection & Response, the guardrails that shape AI use and the monitoring that watches it work from one foundation.
Guardrails apply to the managed browsers and devices agreed for your environment. What's covered is confirmed during scoping and written into your plan.
What's included
One managed platform, configured around your rules.
Discovery of AI in use
See which AI tools your people use, including ones no one approved.
Approved-tool rules
Unapproved AI tools blocked or redirected to approved ones, where your plan includes it.
Sensitive information protection
Sensitive information masked or stopped before it's shared with an AI tool, where your plan includes it.
Prompt injection detection
Attempts to manipulate AI tools with hidden or malicious instructions are detected and flagged for investigation.
Activity records
A record of AI activity that supports investigation and shows leadership how the rules are working.
Implemented and managed for you
Our specialists implement the platform, run it day to day and adjust it as your rules, tools and people change.
How it works
Discover.
We bring AI use on your managed browsers and devices into view, including unapproved tools.
Set approved-tool rules.
We configure which AI tools are allowed, blocked or redirected, to match what leadership agreed.
Protect what's shared.
Prompts are inspected so sensitive information is masked or stopped and manipulation attempts are flagged, where your plan includes it.
Manage and adjust.
We run the platform for you and update the guardrails as your rules and tools change.
What you get

Rules that work in practice.
Your AI rules applied day to day, not left on paper.

Fewer blind spots.
A clear view of which AI tools are in use across your managed devices.

Sensitive information protected.
Information masked or stopped before it reaches an AI tool, where your plan includes it.

Nothing for your team to run.
The platform implemented and managed by InnerCore, on the same foundation as AI Detection & Response.
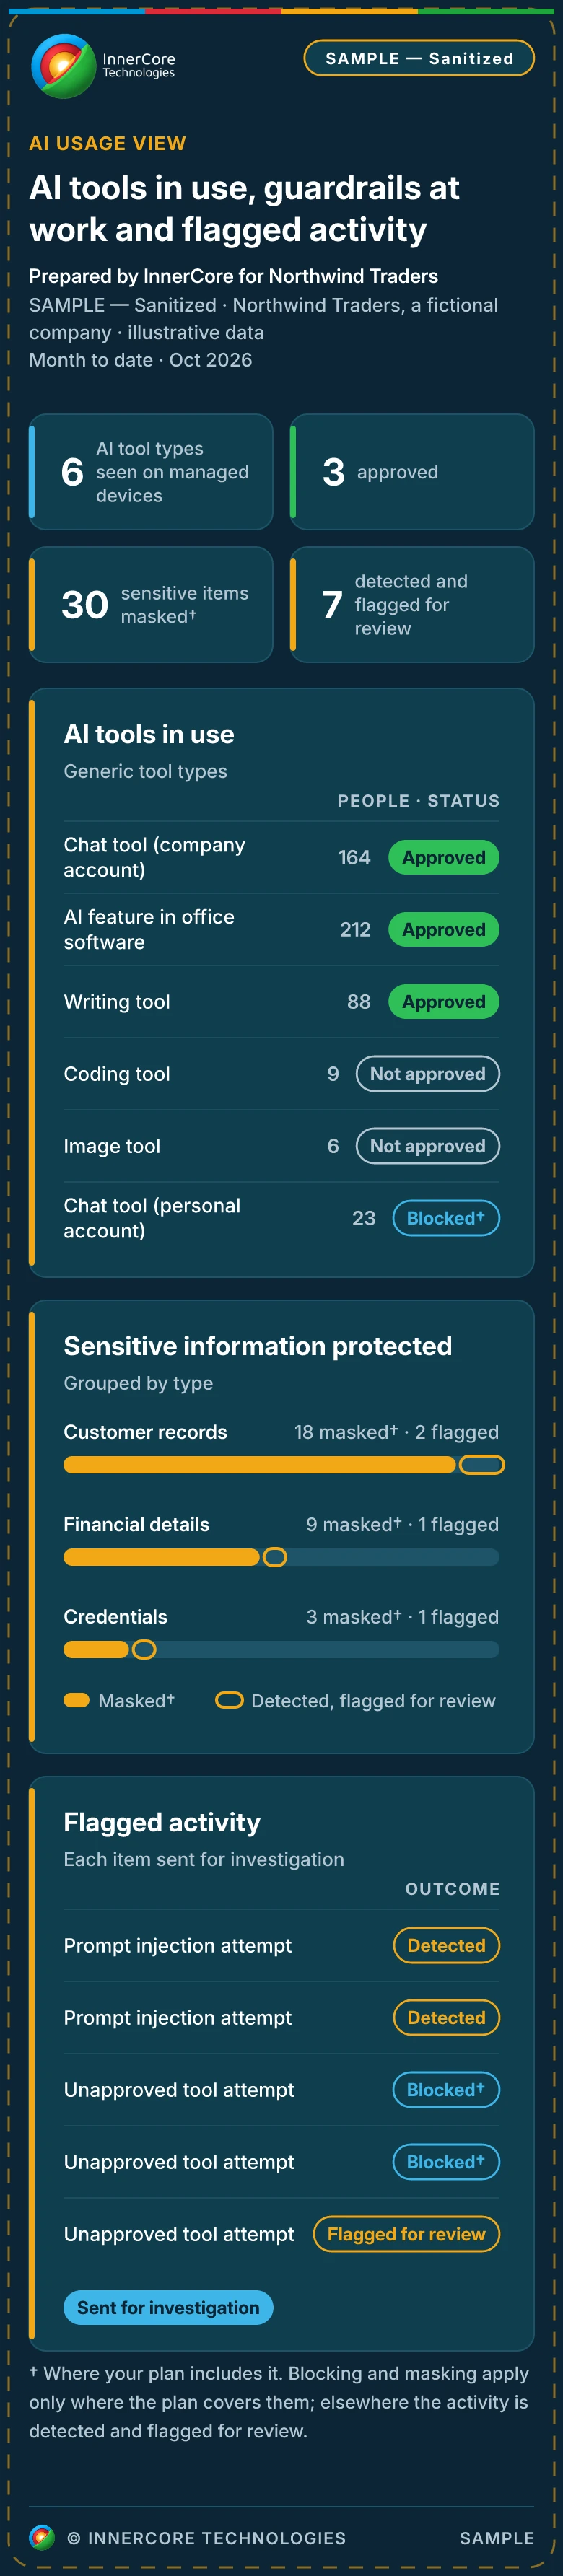
See your guardrails at work
One view of the AI tools in use, which ones are approved or blocked and where sensitive information was protected.
FAQs
How is AI Usage Control different from AI Governance?
AI Governance is where leadership decides the rules. AI Usage Control is how those rules are put into practice through a platform we implement and manage. They work best together, and each can stand on its own.
How does this relate to AI Detection & Response and Data Protection?
The platform behind AI Usage Control also supports AI Detection & Response, which watches for threats and misuse involving AI. Data classification and loss prevention in general stay with Data Protection. AI Usage Control covers guardrails aimed specifically at AI use.
Do we have to run the platform ourselves?
No. InnerCore implements and manages it for you. Your team agrees the rules and stays informed of changes.
Related
AI Detection & Response
Threats and misuse involving your AI tools, detected and handled alongside your other security monitoring.
AI Governance
Clear rules your leadership sets for how AI is used, kept current as the tools change.
Put guardrails on AI use.
Tell us which AI tools your people use and what rules you want in place. We'll show you how we would put them into practice and manage them for you.