Security · Endpoints and servers
Managed endpoint detection and response (EDR) for every covered device.
Every laptop and server is a way into your business. We deploy, tune and manage EDR across your covered devices, and our specialists act on what it finds within the authority in your agreement, including isolating a device.
What's at stake without it.
Laptops and servers hold your files, your logins and your daily work. When one is compromised, the cost lands on the business.

Ransomware and downtime.
One compromised device can be the starting point for encrypted files, locked systems and days of lost work. Recovery takes time, and so does explaining it to clients and your board.
Ransomware was present in 44% of the breaches Verizon reviewed for its 2025 report.

Stolen logins from unwatched devices.
Malware that steals saved passwords and sessions turns one device into a key to your cloud apps. Devices nobody manages make that harder to see.
Of the compromised systems found with corporate logins in stolen-credential logs, 46% were non-managed devices.

Data exposure, insurance and audit questions.
Laptops travel and servers hold the records your clients trust you with. Cyber insurers and auditors ask how endpoints are protected and who watches them, and a vague answer can affect premiums, exclusions or a claim.
Ransomware was again the most pervasive threat to U.S. critical infrastructure in 2024, with complaints up 9% from 2023. FBI IC3, 2024 Internet Crime Report
Is built-in antivirus enough?
The antivirus built into your operating system is a useful baseline. On its own, though, it mainly looks at one device at a time, and its alerts wait for someone to notice them. Many modern attacks use stolen logins and legitimate tools that look normal to a file scan. That's why we deploy managed EDR: it records how each device behaves, flags suspicious activity, and gives our specialists the means to isolate a device.
What it looks for
- Built-in antivirus only
- Mainly known malicious files on each device
- Managed EDR from InnerCore
- Suspicious behavior as well as known threats: unusual processes, scripts and activity patterns
What it records
- Built-in antivirus only
- Limited history of what happened on the device
- Managed EDR from InnerCore
- A record of device activity that specialists use to investigate what happened and where it started
When something is found
- Built-in antivirus only
- An alert on one device, waiting for someone to see it
- Managed EDR from InnerCore
- Detections reviewed by our specialists and acted on within the authority set in your agreement
Containing a device
- Built-in antivirus only
- Someone on site has to step in
- Managed EDR from InnerCore
- A compromised device can be isolated from the network remotely
Policy and tuning
- Built-in antivirus only
- Default settings, managed alongside everything else on IT's list
- Managed EDR from InnerCore
- Policies set, tuned with the vendor and kept current by our specialists
Coverage
- Built-in antivirus only
- Hard to confirm which devices are protected and reporting
- Managed EDR from InnerCore
- Coverage tracked across covered devices, with gaps chased down and exceptions documented
| Item | Built-in antivirus only | Managed EDR from InnerCore |
|---|---|---|
| What it looks for | Mainly known malicious files on each device | Suspicious behavior as well as known threats: unusual processes, scripts and activity patterns |
| What it records | Limited history of what happened on the device | A record of device activity that specialists use to investigate what happened and where it started |
| When something is found | An alert on one device, waiting for someone to see it | Detections reviewed by our specialists and acted on within the authority set in your agreement |
| Containing a device | Someone on site has to step in | A compromised device can be isolated from the network remotely |
| Policy and tuning | Default settings, managed alongside everything else on IT's list | Policies set, tuned with the vendor and kept current by our specialists |
| Coverage | Hard to confirm which devices are protected and reporting | Coverage tracked across covered devices, with gaps chased down and exceptions documented |
What you get
One managed layer across the devices your business runs on.

Behavior monitoring.
EDR watches how processes, scripts and users behave on each covered device, so suspicious activity is flagged even when no known malicious file is involved.

Device isolation.
A compromised device can be cut off from the network remotely while it's investigated, which helps keep a problem on one machine from becoming a problem across many.

Ransomware protection.
Monitoring designed to help protect against viruses, malware and ransomware, with suspicious activity flagged for our specialists to act on.

Device health and coverage.
We confirm every covered device has protection installed and reporting, and we chase down the ones that drop off.

Policy control.
Endpoint policies set to your baseline, quarantine managed and security updates kept current, with the vendor engaged on tuning.

Managed EDR.
Deployment, removal of legacy tools where needed, and day-to-day management by our specialists, with detections reviewed and reported.
Covered devices watched, and detections reviewed by specialists.
Deployed, tuned and watched by people who act on what it finds.
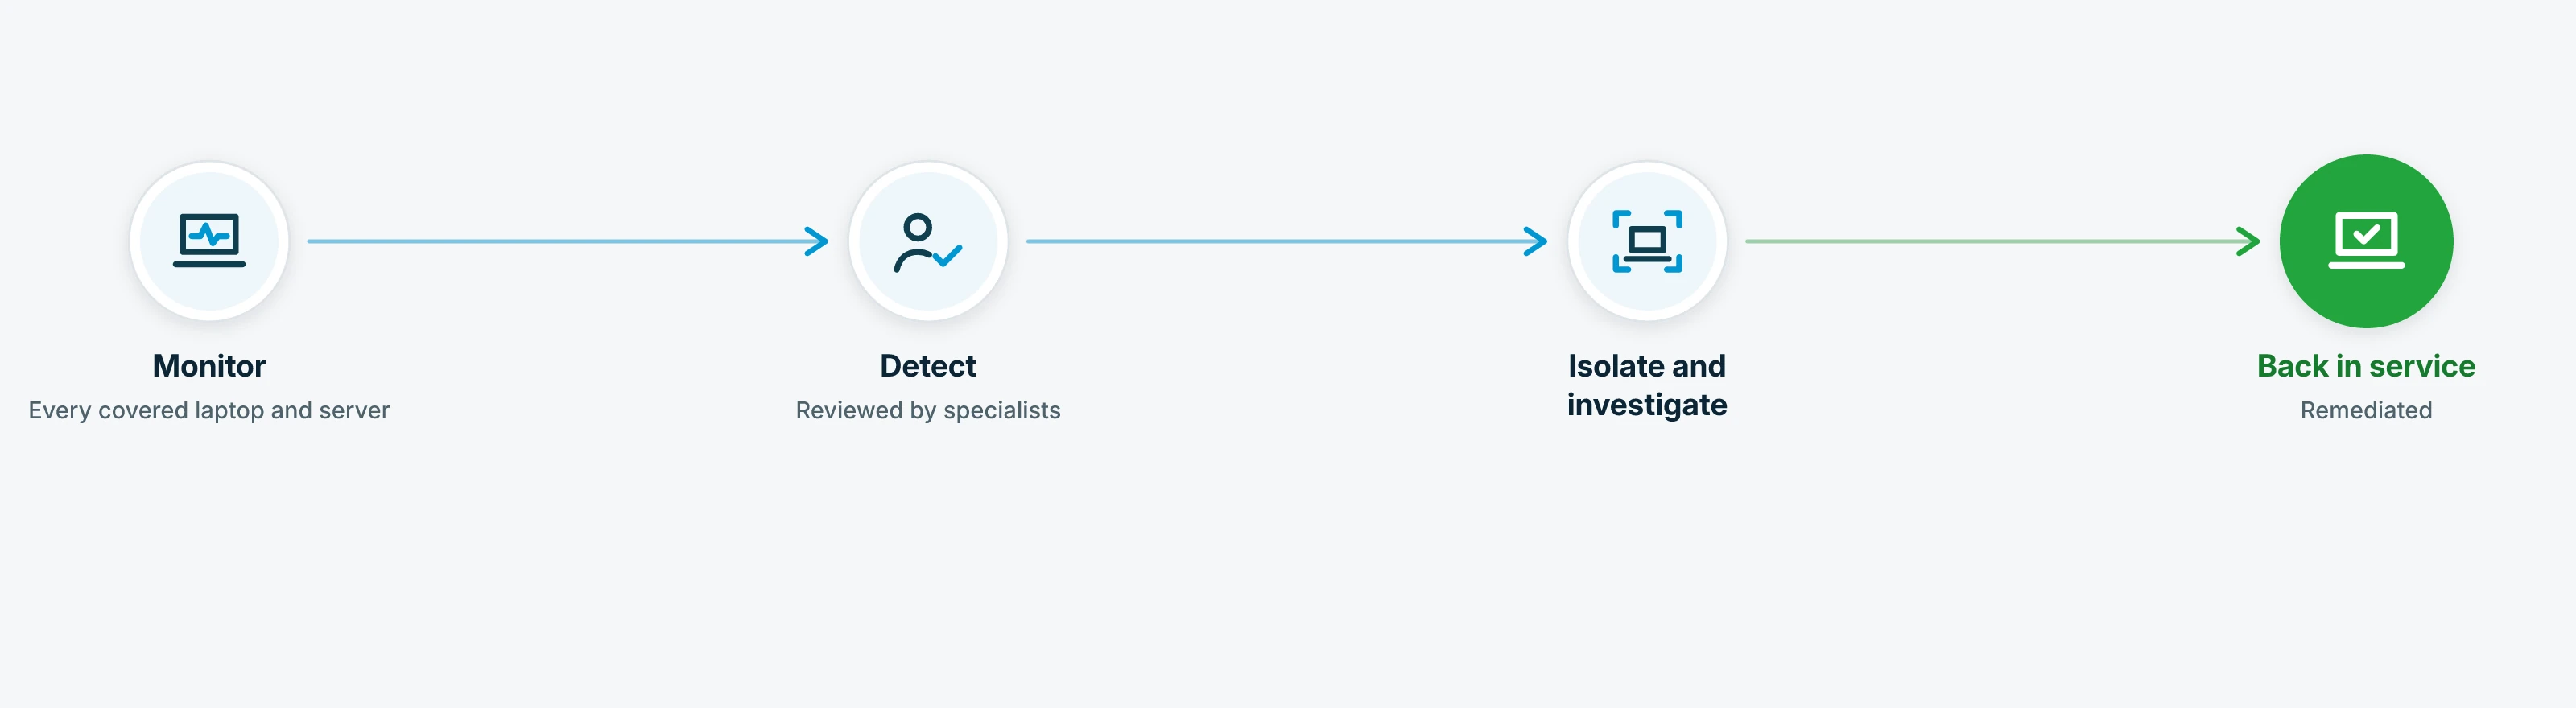
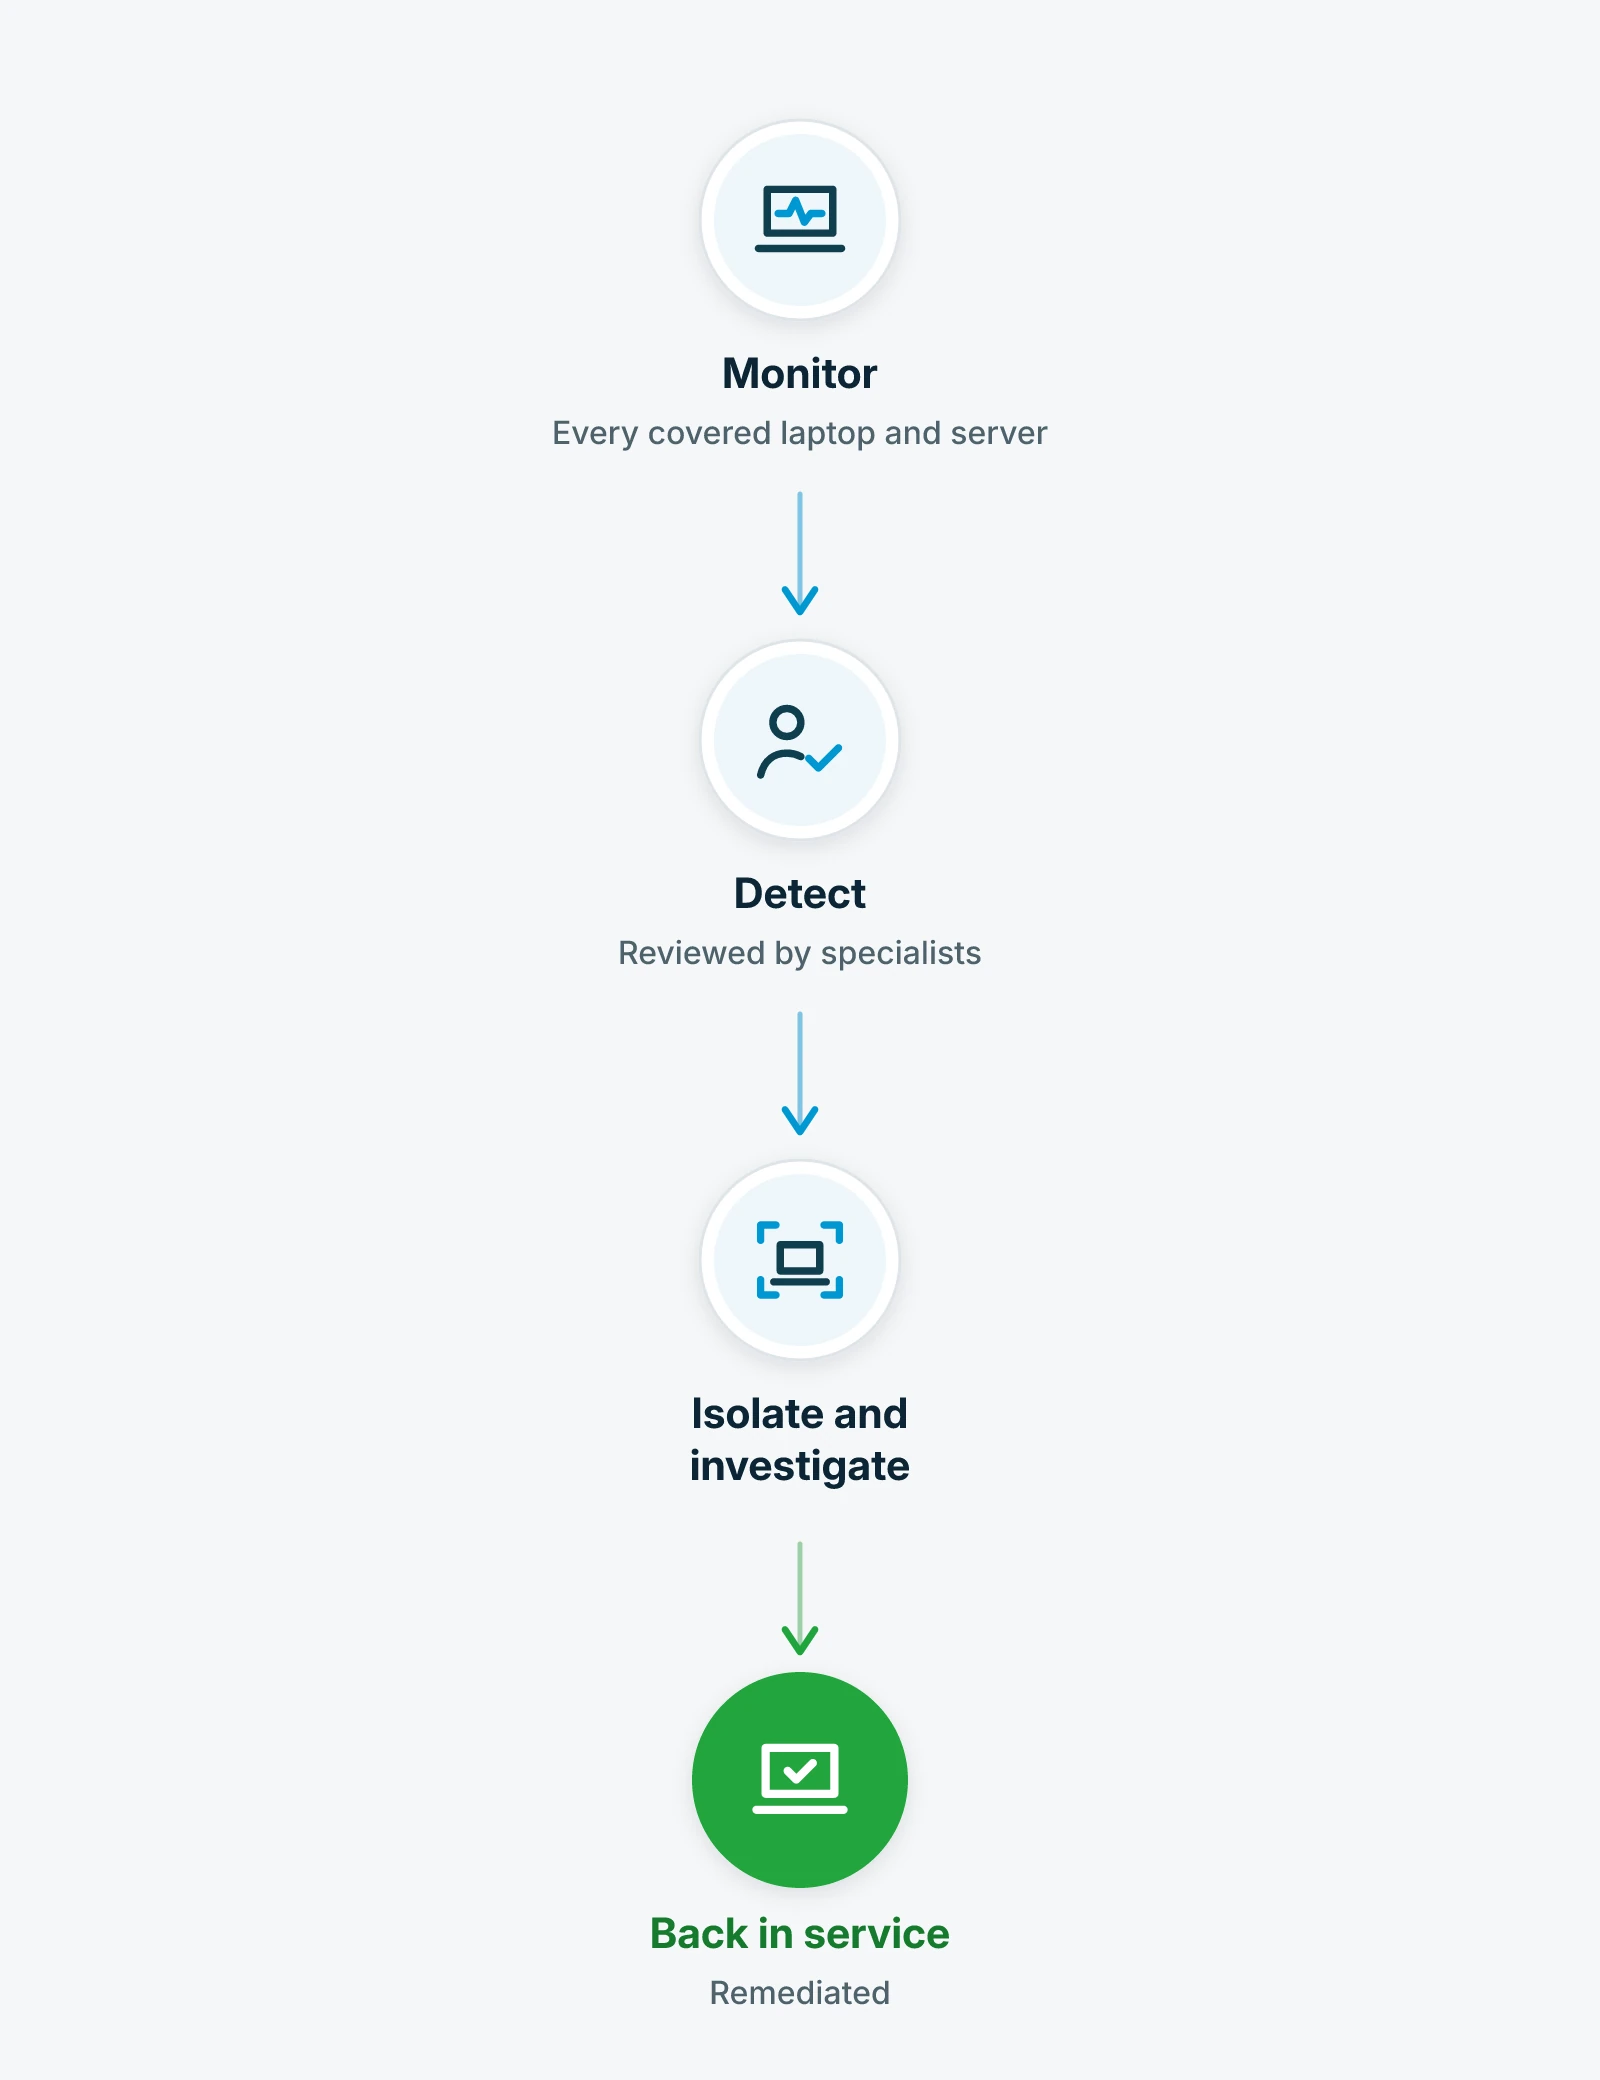
We start by taking inventory of your covered devices and agreeing the policy baseline with you. We deploy the EDR agent, remove legacy tools where needed and confirm every device is reporting. Then we tune policies with the vendor, manage quarantine, keep security updates current and review detections. When something is confirmed, we isolate the device and investigate, and tell you what happened and what changed, within the authority in your agreement.
When your plan includes 24/7 Monitoring, Detection and Response, endpoint detections are monitored around the clock, with response within the authority and hours set in your agreement. Specialists connect signals from your devices, email, identities and network into one picture. How far we act on a confirmed threat is limited to isolating a device (and securing an account when identity signals are in play), as written into your agreement and confirmed before you sign.
We build on industry-leading, best-of-breed security platforms, and when one isn't the right fit for your environment, our specialists vet and deploy one that is.
Our specialists look at your devices, the protection you already own and how your teams work, then recommend the endpoint protection your environment needs, as part of a plan we agree on together. Never a forced bundle.
Devices are where work happens. The other layers protect everything around them.
EDR protects the device itself. The layers around it connect what it sees, protect the logins on it and check mail before it reaches your people.
Managed Detection and Response
Our security operations specialists connect signals from your devices, email, identities and network into one picture.
Identity & Access Security
Protect passwords, admin rights and sign-ins, and harden Microsoft 365 against account takeover.
Advanced Email Security
Checks mail before it reaches your people, on Microsoft 365 or Google Workspace.
FAQs
We already have antivirus. Isn't that enough?
Antivirus is one layer. Managed EDR adds behavior monitoring, remote isolation and specialists who review what it finds. Many incidents also start with email or a stolen login, so we connect endpoint protection with the other layers.
Is this the same as device management?
No. Endpoint security protects devices from threats. Configuration, software and patching live under Desktop & Server Management, and the two link together.
What happens when a device is isolated?
The device is cut off from the network so it can't reach other systems, while our specialists keep the connection they need to investigate. We tell you what was found and what we did within the authority in your agreement.
Will you remove infections that are already there?
Threats already on a system when protection is installed may need additional work to remove, which we scope and quote separately.
Can EDR promise we'll never have an incident?
No security product can promise that, especially if someone deliberately installs malicious software. That's why endpoint security is one layer in a defense in depth, with resilience built in behind it.
Related services
- Desktop & Server Management
Configuration and patching
- Advanced Email Security
checks mail before it reaches your people.
Know every device is covered.
Let's look at your endpoints together: which devices are protected and reporting, how your current protection is set, and what our specialists would change first.