

Vendor management
We deal with your phone, internet, copier, software and hardware vendors for you, with your written authorization.
Protect
Checks mail before it reaches your people, on Microsoft 365 or Google Workspace.
Desktops, laptops and servers protected, tuned and watched by specialists.
Protects accounts, passwords and admin rights, with ITDR when it's in your plan.
Detect & Respond
Around-the-clock monitoring, detection and response, scoped to your agreement.
Experts search for hidden threats that never raised an alarm, if in your plan.
Respond & Recover
Help to contain ransomware or account takeover and get your business running.
AI Security & Governance
AI Security overviewAI visibility, clear rules and response to AI threats and misuse
AI Security
AI threats and misuse, investigated and handled
Clear AI rules your leadership owns
Guardrails that put your AI rules into practice
Managed IT
Managed IT overviewService desk, devices, Microsoft 365 and networks, run for you or with your IT.
Support
One place for your people to get help, with every issue worked to resolution.
Desktops, laptops and servers kept healthy, monitored, patched and documented.
Business calling in Microsoft 365, set up properly and supported after launch.
Systems
 24/7 Server and Network Monitoring
Servers and network watched around the clock, with fixes set by your agreement.
The systems behind sign-in, email delivery and your websites, kept documented.
Your Microsoft 365 and Azure run by specialists, so settings don't drift.
Switching, wireless, WAN and VPN, documented, monitored and maintained.
Advisory
Advisory overviewSenior security and technology guidance for leadership. We advise; you decide.
Managed IT
The everyday IT your business runs on: a help desk for your people, servers and desktops kept running, networks managed, Microsoft 365 looked after and backups checked. Fully managed or co-managed, shaped with our specialists around what your business needs.


One partner accountable for IT and security.
Patching, monitoring and documentation run to a written standard.
A clear, written split of who does what.
Vendors handled for you, with your written authorization.
A dedicated senior account manager and regular account reviews.
The work
Managed IT is the foundation our security work runs on. We take on the daily load, from the help desk and patching to monitoring, Microsoft 365 and networks, and run it to a written standard.
Fully managed or co-managed, together we agree on who leads each activity, so the split is clear from day one.
Every plan is built around your team and the tools you already run, never a forced bundle.
Bigger changes are scoped as one-time projects outside your agreement.
When one company runs your IT and another protects it, problems fall into the gap between them. At InnerCore, the people who keep your systems running work inside the same model as the people who secure them: shared documentation, shared monitoring and one escalation path. A patch, a firewall change or a suspicious alert is handled by one partner who sees the whole picture.
A help desk your people can reach by portal, email or phone, with issues worked through to resolution.
Servers, desktops and laptops kept running, patched and monitored.
Microsoft 365 and Azure looked after day to day: users, licenses, devices and settings.
Phone numbers, call routing and devices, set up and supported in Microsoft 365.
Sign-in, email delivery and website certificates kept working behind the scenes.
Switches, Wi-Fi, internet circuits and remote-access connections monitored and maintained.
Migrations, upgrades and replacements, scoped and approved before work starts.
We deal with your phone, internet, copier, software and hardware vendors for you, with your written authorization.
A dedicated senior account manager and regular account reviews. For technology plans and budgets, our IT Strategy & Budgeting advisors (often called a virtual CIO) build the roadmap with you.
Fully managed or co-managed, the split is agreed and written down before we start.
Who runs day-to-day IT
Your IT staff
Help desk, patching and monitoring
Change approval
Account management
| Item | Fully managed | Co-managed |
|---|---|---|
| Who runs day-to-day IT | InnerCore, to a written standard | Shared, with a written Lead / Support / Informed split |
| Your IT staff | Not required | Keep ownership and relationships |
| Help desk, patching and monitoring | InnerCore | Usually InnerCore leads |
| Change approval | Agreed with you | Often your team leads |
| Account management | Dedicated senior account manager and regular account reviews | Dedicated senior account manager and regular account reviews |
At the start, we agree who leads incidents, changes and escalations, and we write it down.
Each activity is assigned as Lead (accountable for delivery), Support (assists or approves) or Informed (kept up to date). For example, we lead the help desk, patching and vendor management, and your team leads line-of-business applications and change approval. how the Lead / Support / Informed model works
We review your environment, your team and the tools you already run, then agree with you on what's in scope and who leads each activity.
We set up monitoring, patching and documentation to our written standard, and show your people how to reach the service desk.
We run the day-to-day work, handle your vendors and review the service with you at regular account reviews.
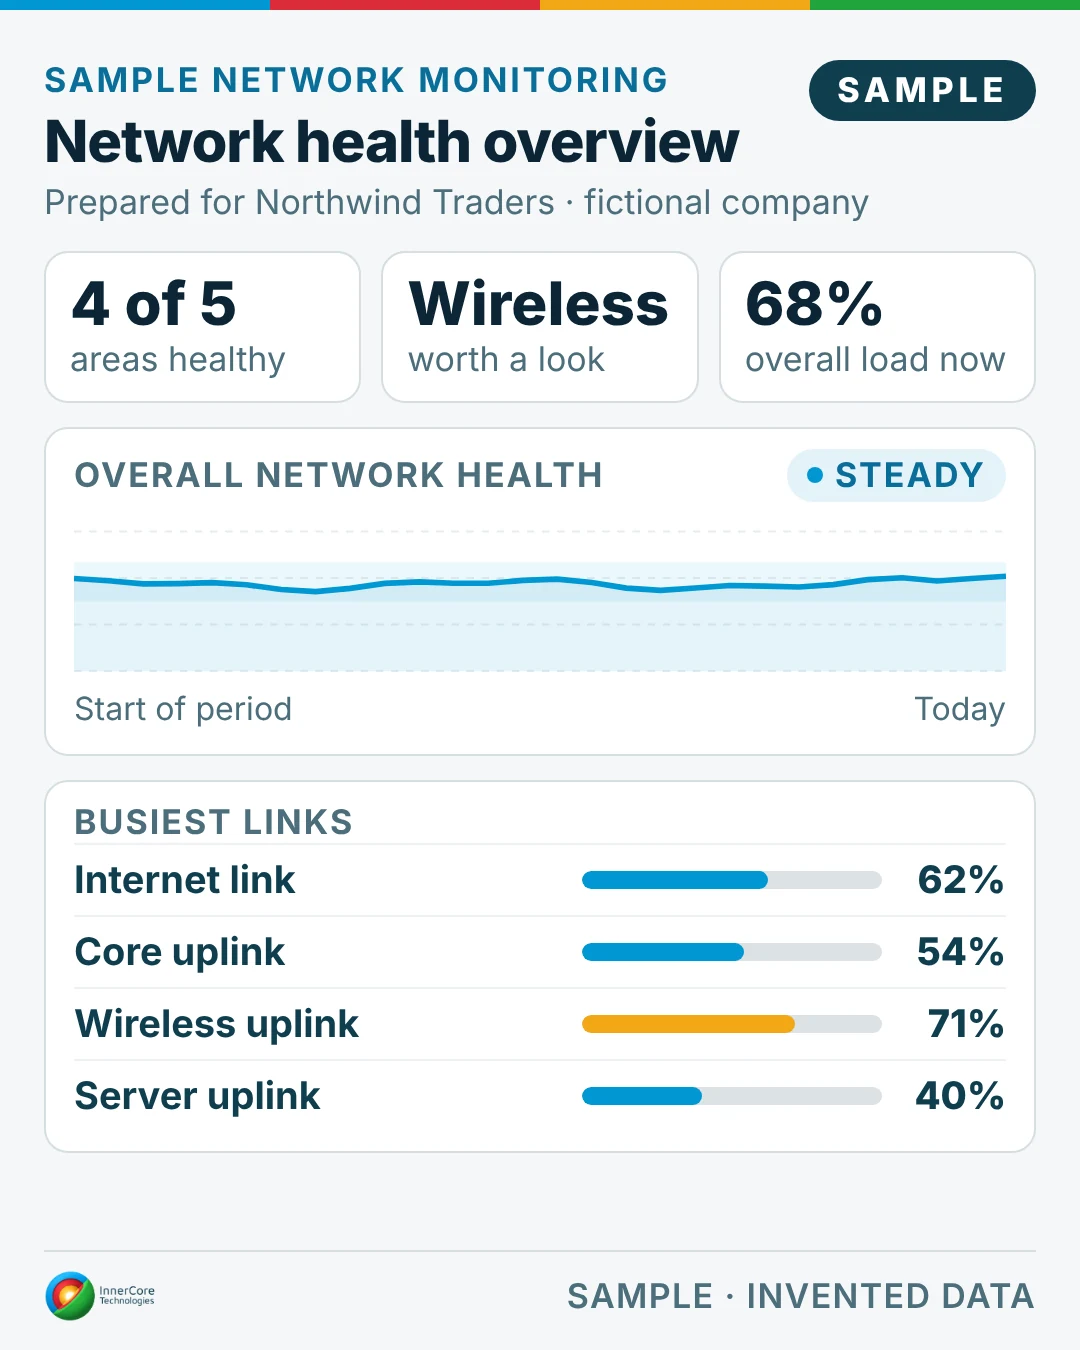
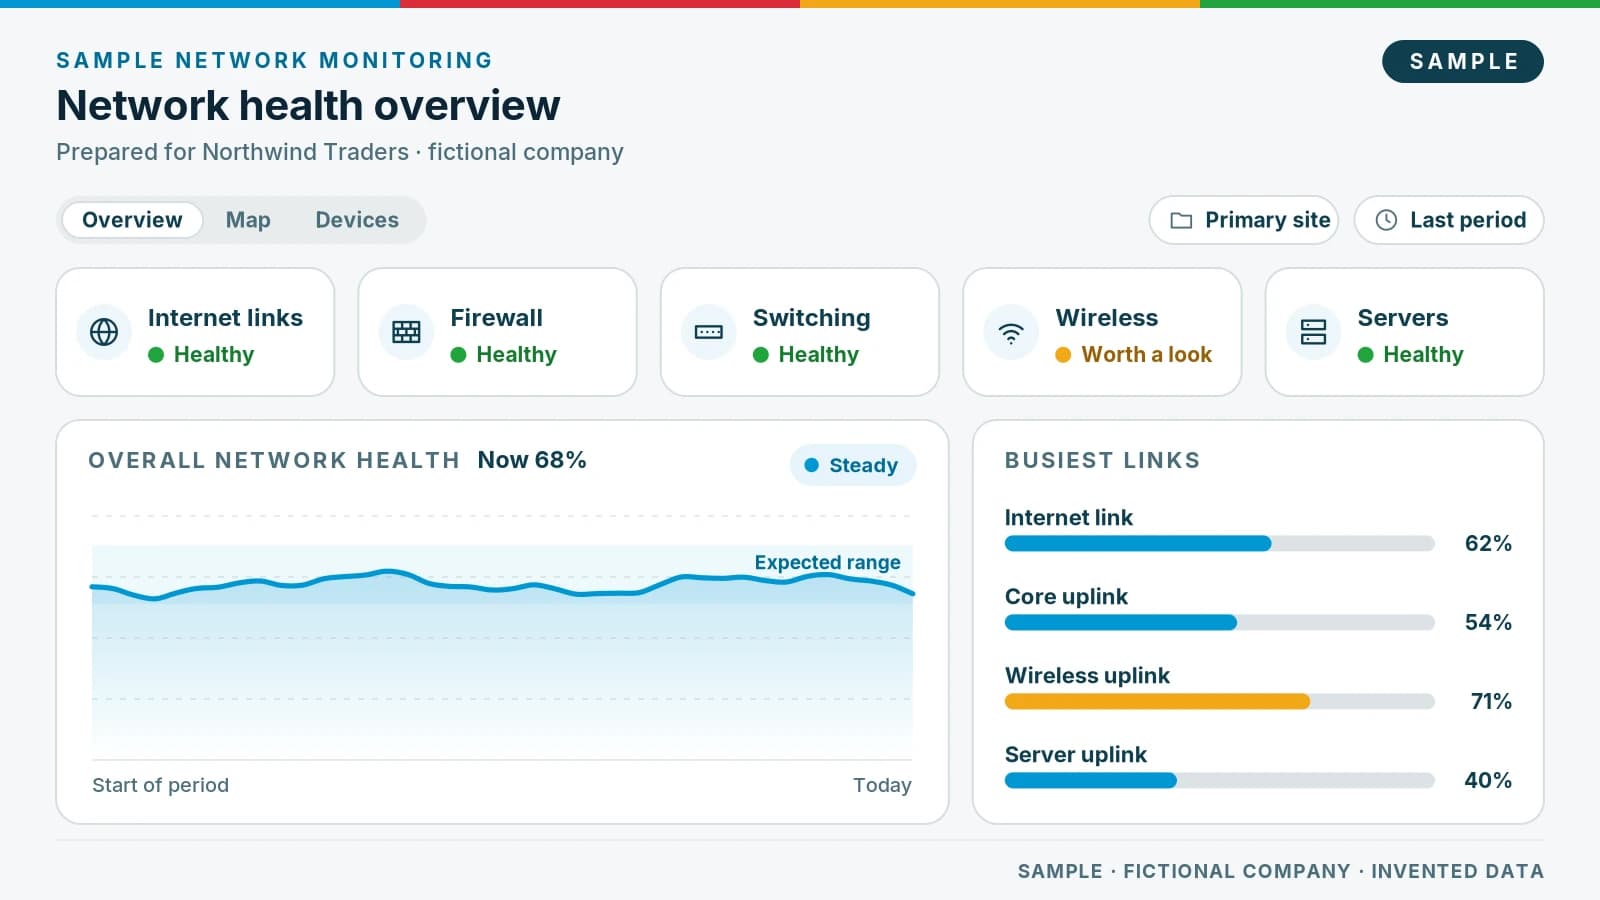
Monitoring across your network, servers and devices, with anything worth a look raised early and followed up. The views below are samples made for a fictional company.
Servers and network watched around the clock, with fixes set by your agreement.
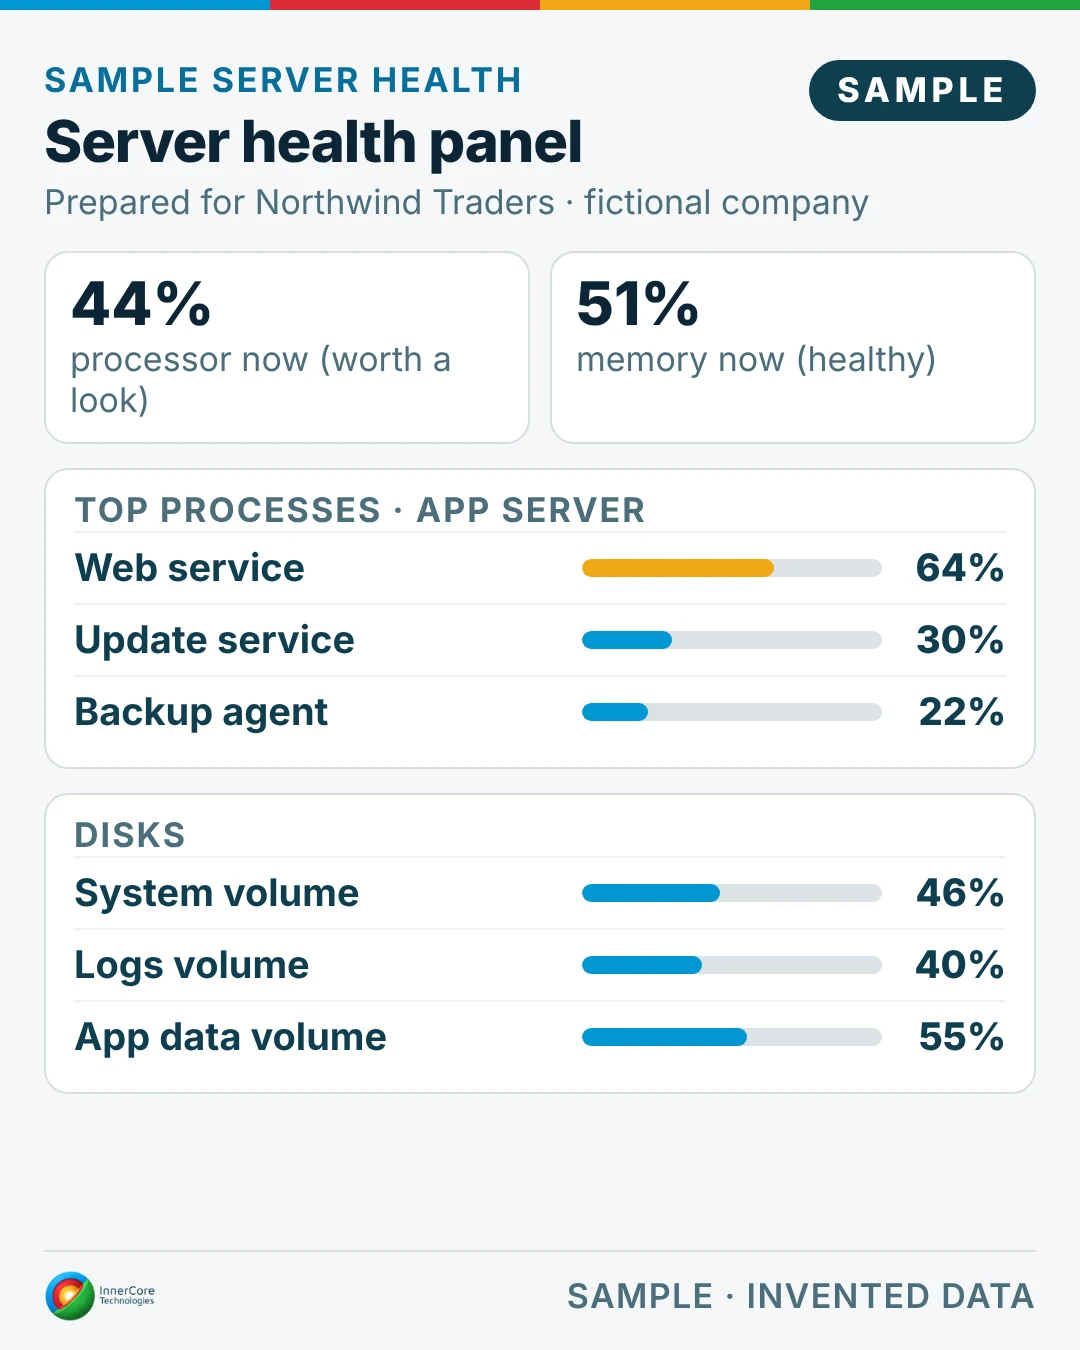
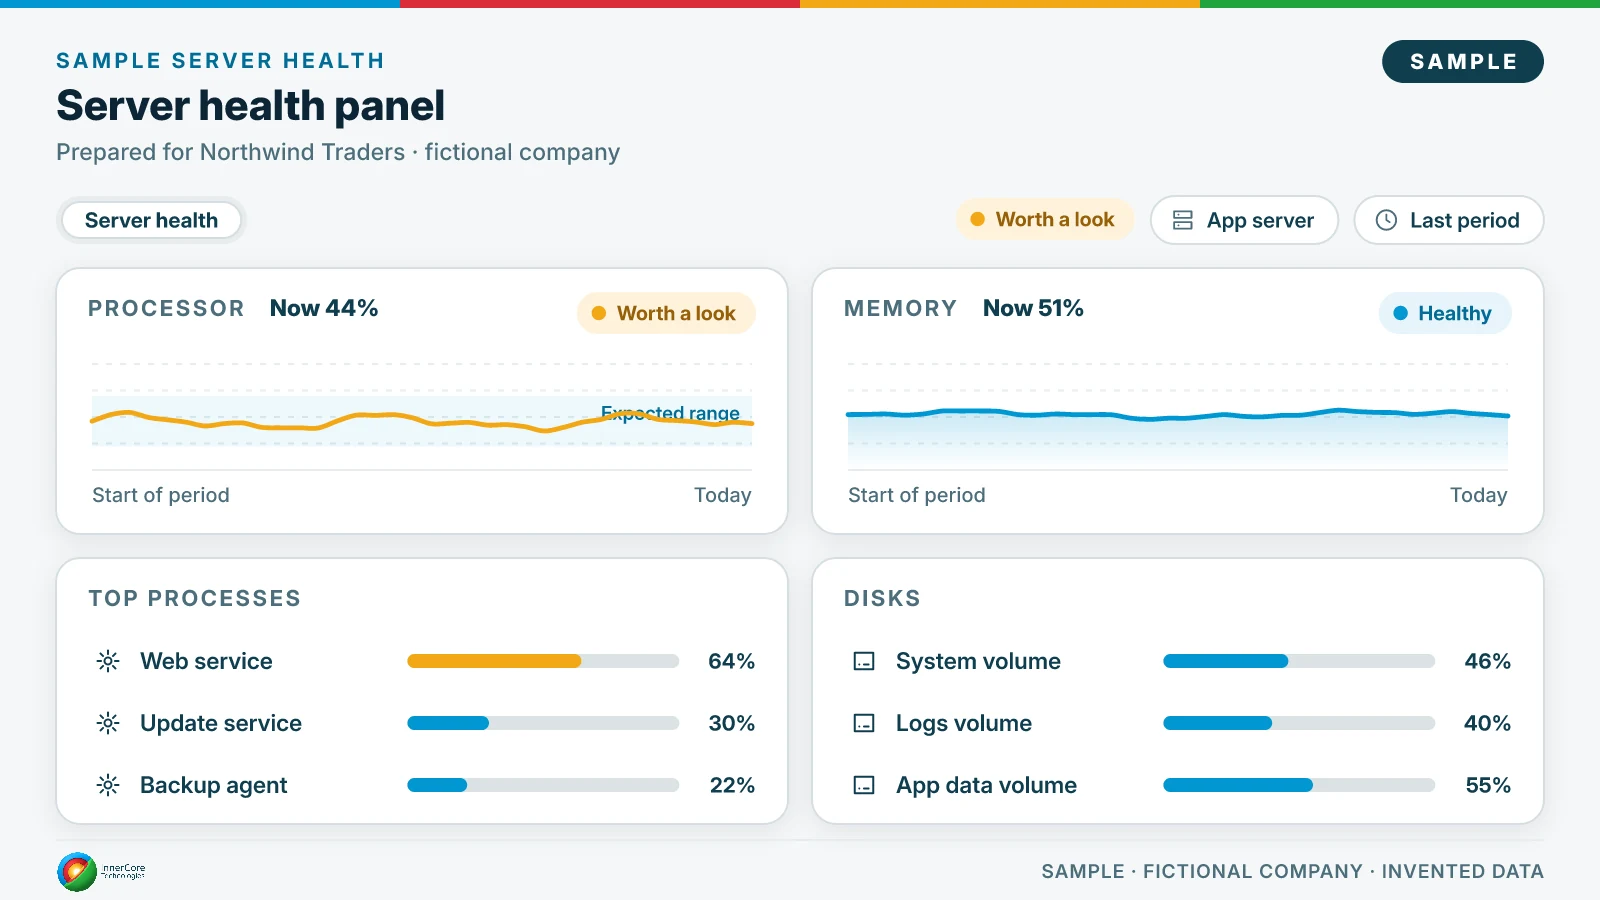
Sample server health panel for the fictional company Northwind Traders: processor 44% (worth a look), memory 51%, top processes and disk use with values.Sample server health panel for the fictional company Northwind Traders: app server processor at 44% (worth a look) and memory at 51% (healthy), top processes (web service 64%, update service 30%, backup agent 22%) and three disks at 46%, 40% and 55% used., slide 1 of 3
Migrations, upgrades and replacements are scoped and approved before work starts, then run by the same people who know your environment. For technology planning and budgets, our IT Strategy & Budgeting advisors (often called a virtual CIO) build the roadmap these projects come from.
EXAMPLE: illustrative only, not a real customer.
A healthcare group's two-person IT team was buried in tickets, patching ran late, and their outside security provider rarely spoke to them.
We set up co-managed IT with a written split: InnerCore led the help desk, patching and vendor management, and the internal team kept line-of-business applications and change approval. Security and IT now run in one model.
Patching on schedule, one partner accountable for IT and security, and an internal team back on the projects leadership asked for.
Yes. We strengthen your IT team. We don't replace it. Your person keeps ownership and relationships, and we take on the work they can't get to, from patching and monitoring to the help desk.
Fully managed means InnerCore runs the IT services in your agreement, to a written standard. Co-managed means we work alongside your IT staff or other providers, with every activity assigned as Lead, Support or Informed. Our specialists help you work out which model fits, and we write the split down before we start.
Your agreement lists what is covered and up to what quantities. Repairs, projects, hardware, licensing and onsite work beyond your agreement are quoted and approved by you first.
We deliver remotely by design, so your service runs the same way wherever your people work. When a project truly needs on-site work at an office or data center, it's either defined in your agreement or scoped and billed separately.
Backup is an optional service, not part of every plan by default. If we agree on it together during your assessment, it runs as Backup & Disaster Recovery within our security services, with resilience built in through immutable, ransomware-protected backups. Managed IT then checks that your server backups complete and fixes any that fail.
Dedicated security specialists on our team handle your security services, and our managed IT engineers run your systems. Each team focuses on its own work, and they share the same documentation and one escalation path, so you always have one clear place to go.
a dedicated team for one technical role
Talk with our specialists about your environment and your team, and we'll show you how fully managed or co-managed IT would run alongside the security that protects it.
This site uses analytics cookies only if you accept. Privacy policy


